introducing

Defend with one accurate agentic system

Mate unlocks a deep understanding of your organization and turns it into purified knowledge so AI agents take the right action, on time, across every security use case.
Get a demo
Built for agents. Trusted by enterprises.

“I was impressed with how accurate Mate’s verdicts are. Mate covered our entire stack within days, including tools we weren’t watching, and it investigates every alert with the full evidence laid out. The rollout was smooth, and Mate delivered value much faster than I expected.“
Derek Stephenson
Derek Stephenson

Chief Information Security Officerֿ, Demandbase

“Before Mate, we had to make tradeoffs about which alerts got investigated. Now every alert gets a thorough investigation, so nothing slips through and our risk exposure shrinks. What sets Mate apart is the infrastructure behind each investigation. Its agents are grounded in a deep understanding of our environment, so the conclusions are consistent, accurate, and something my team can act on with confidence.“
Tanner Randolph
Tanner Randolph

EVP, CIO, CISO, Applied Systems

“In a banking environment, we need tools that can act as a true security companion: flexible enough to assign complex work to, but accurate enough to trust. Mate's agents do just that - they maintain exceptional accuracy, while automating the metadata and reporting we need for regulators. Mate truly helped us move from manual analysis toward scalable processes.“
Gavin Grisamore
Gavin Grisamore

Chief Information Security Officer, Lead Bank

“Mate goes beyond processing alerts - it continuously learns how our environment operates. It becomes more attuned to what matters most, helping our team focus on the work that truly strengthens our security posture.“
Anthony Candeias
Anthony Candeias

Chief Information Security Officer, Bridgewater Associates

“Mate significantly helped us reduce our MTTR. It delivered deep investigative insights and incident summaries in minutes. It has also been instrumental in helping our analysts grow and operate at a more senior level. The depth and quality of investigation it provides go far beyond anything else we’ve seen.“
Matthew Wilmot
Matthew Wilmot

Chief Information Security Officer, Merlin Entertainments

“Mate’s AI driven SOC automation brings real operational impact, enabling security teams to automate investigations and focus on the risks that truly matter.“
Hadar Michaelis
Hadar Michaelis

Group CISO & Head of Group TISO, OCBC

“Mate represents a fundamental shift for our internal SOC. It drove a measurable drop in both Time to Acknowledge (TTA) and Time to Resolve (TTR). We have successfully moved nearly 100% of our investigations into Mate, federating data across our entire stack into a single centralized hub. With Mate handling the heavy lifting of enrichment and investigation, we can upskill our service desk staff into SOC roles and we can save costs by transitioning away from high-cost external monitoring models.“
Pieter VanIperen
Pieter VanIperen

Chief Information Security Officer, AlphaSense

“As an MSSP, the customers you can serve are typically defined by what security stacks your analysts have experience with. Mate unlocked this for us: we are now fully stack agnostic. We hire an analyst, onboard them to Mate, and provide high quality service to any customer, on any stack, from day one. Mate is the mediator. Our addressable market just got exponentially larger. Beyond this, Mate dramatically reduced our MTTR and time spent per incident, which means we deliver superior quality of service to every customer we work with.“
 Alexander Kraus
Alexander Kraus

Chief Technology Officer, Water-IT

Redefining Security Operations

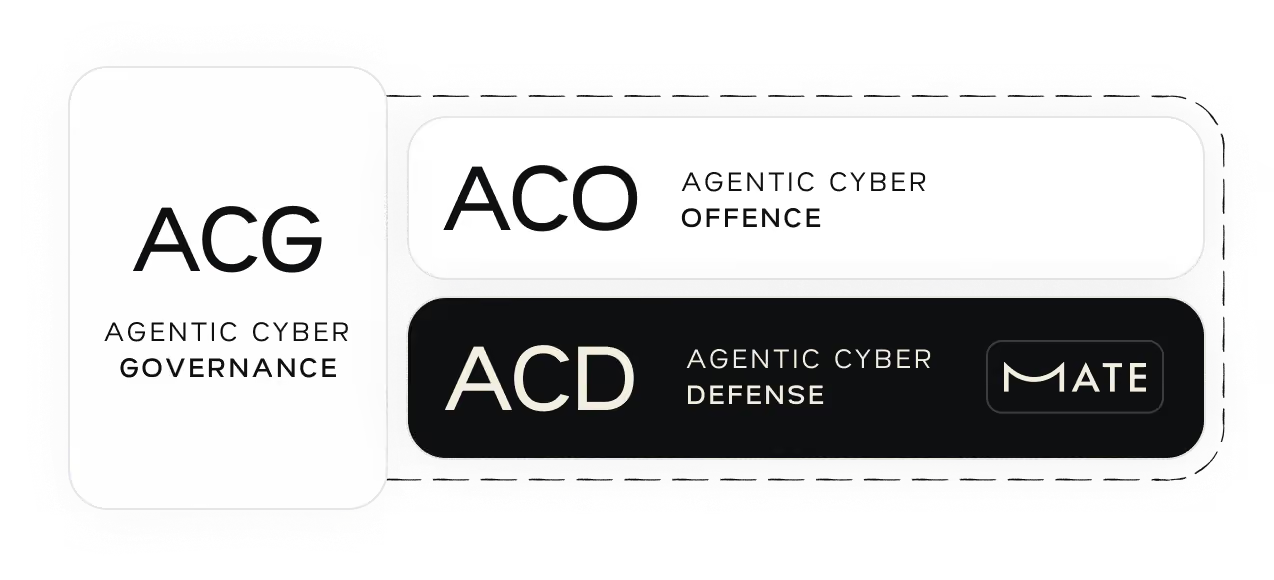
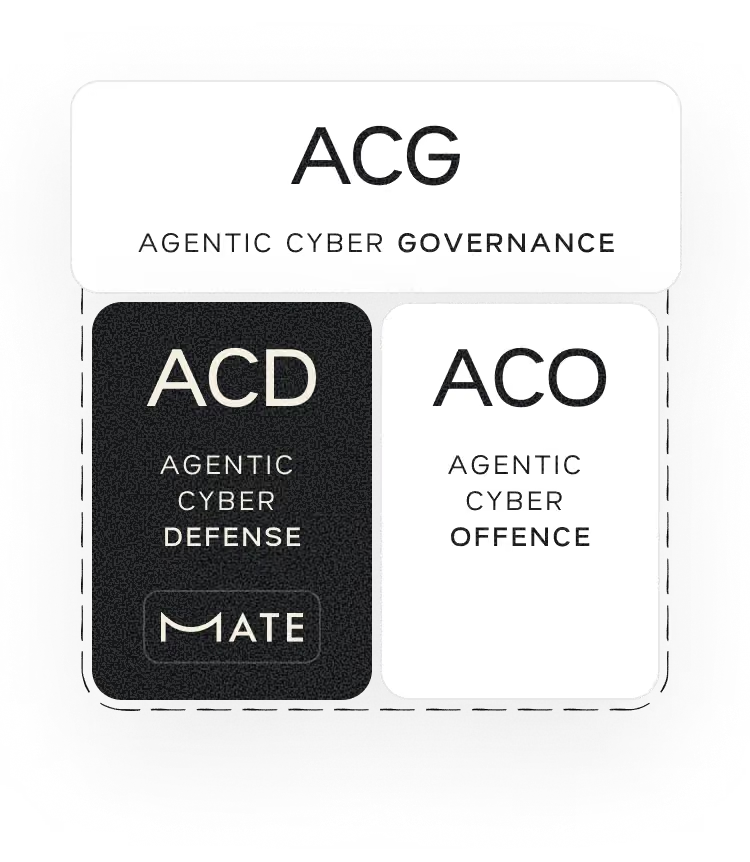
The cybersecurity market is splitting into three:
Governance (ACG)

keeps AI agents in check: what they can touch, and who’s accountable.

Offense (ACO)

thinks like an attacker to find the gaps first.

Defense (ACD)

protects the business.

Mate is ACD: built from day one for AI agents to reason on, and to stay accurate in complex environments.
ACD
agentic
cyber
defense

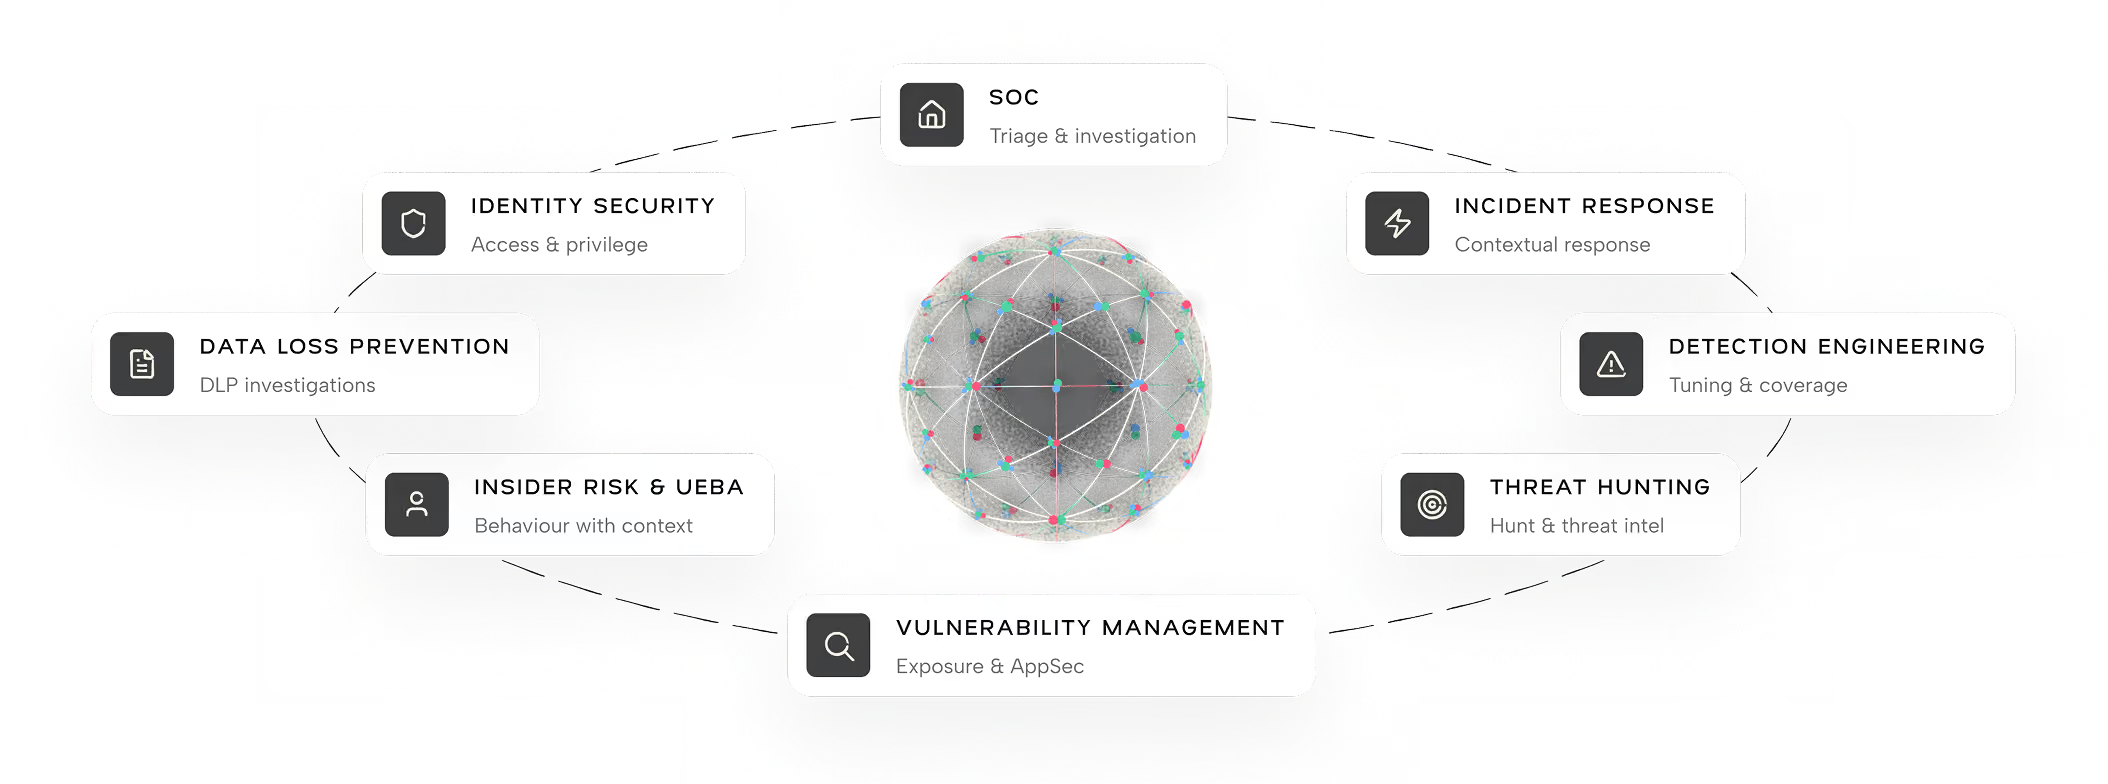
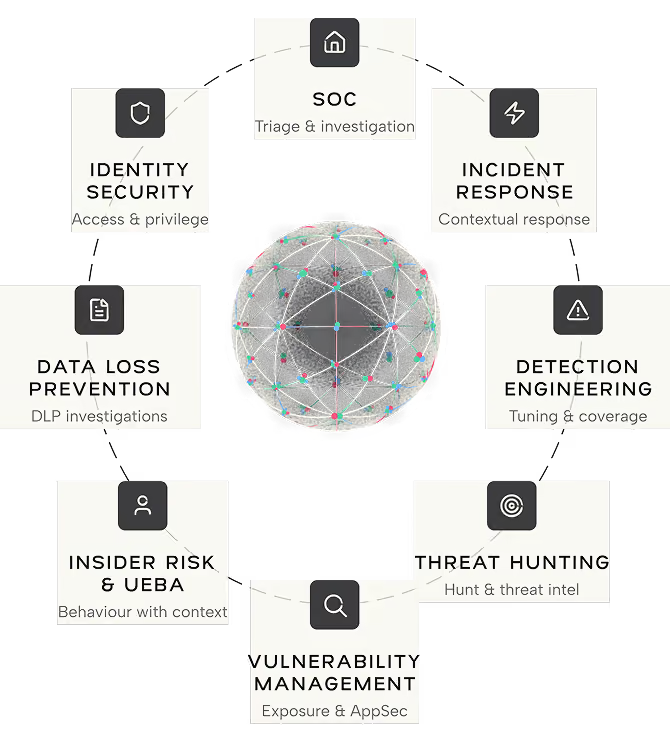
One Unified Agentic Cyber Defense System
SOC

Triage & investigation

Threat Hunting

Hunts & threat intel

Incident Response

Containment across tools

Insider Risk & DLP

People & data in context

Exposure Management

Attack surface & vulnerability

Detection Engineering

Tuning, health & coverage

Security Engineering

Tool & data-source health

Security Architecture

Learn from every case to prevent tomorrow’s attack

Insider Risk & DLP

People & data in context

Exposure Management

Attack surface & vulnerability

Detection Engineering

Tuning, health & coverage

Security Engineering

Tool & data-source health

Security Architecture

Learn from every case to prevent tomorrow’s attack
98.7%
Accuracy with Mate
97%
False-Positive Auto-Closure
6.1X
Investigation Coverage

Frontier models alone can’t make
accurate security decisions

Accuracy gain with Mate by frontier models

Accuracy gain with Mate by frontier models

Gemini 3.8 Flash
69%
+30points
GPT-6.1 Sol †
51%
+48points
Claude Opus 5.5
72%
+27points
Claude Sonnet 5.5
71%
+27points
0%25%50%75%100%
98.7%
Model alone: not accurate enough
Gap closed by Mate
Mate: best frontier model per task
Basic harness
Codex for Gemini 3.8 Flash, GPT-6.1 Sol and Claude Sonnet 5.5; Claude Code for Claude Opus 5.5 (best of the two per model). † GPT-6.1 Sol on a subset.
Accuracy on 7,200 alerts

Frontier models were not built for security
It's context-blind.

Generic AI meets your organization fresh every time, with no memory of what's normal or what happened before. Across an enterprise, no conclusion holds up at scale.


It's disconnected.

Generic AI operates tool by tool, with no shared context across your stack. Signals get lost in the handoffs, and those gaps become blind spots attackers walk through.
It breaks.

A generic model states its conclusion with equal confidence whether it verified the evidence or guessed, so one bad call can propagate across every asset it touches.
THE MECHANISM

The accuracy chain

AGENTIC CYBER DEFENSE SYSTEM
Every signal, log, and event is collected.
It’s then run through cleanup, normalization, and correlation. Only clean, relevant data is included.
We store the data as entities and relationships. Our reason mining engine keeps the underlying reason behind each conclusion.  Those memories reveal an understanding that wasn’t available before, backed by evidence.
Powered by
Reason Mining
That understanding, together with guardrails and guidance, gives agents a source of truth on when and how to act, and what the blast radius would be.
Powered by
Gamebooks
Agents take the surgical, right action, eliminating the risk.
Powered by
CPR
Every outcome is scored and fed back into the system, sharpening what counts as normal and feeding the next cycle of collection.
Powered by
CD/CR

Accuracy that runs deep

1

The Right Action

What agents do, visible and on time
2

Purified Knowledge

Validated, evidence-backed,
clean, and shared by every agent.
3

Deep Understanding of
your environment

Assets, identities, ownership, and
your team's judgment.
Future proof, today
It scales

Every use case runs on the same foundation, so entities grow with the organization and each new one reuses what's already there.
It's fast

Knowledge is ready before the incident, so agents act on their own when it's safe and new use cases go live faster.
It lasts

While models change, Mate's foundation stays, bringing the proprietary, evidence-backed knowledge that keeps growing.
FAQs

What happens when my senior analyst leaves? Does Mate preserve their knowledge?
Yes. Their expertise stays - for both agents and analysts. When a senior analyst leaves, their investigation knowledge stays too: how to handle DLP alerts, check custom apps for user context, and navigate your compliance portal. These workflows become lasting organizational capabilities. Your SOC capability compounds instead of resetting with every departure.
I already have automation - why would I buy another tool?
Your SOARs, SIEMs, and automations assume security is predictable - it’s not. They break when things change. Mate elevates your team by using organizational wisdom to adapt in real time - pulling context, correlating data, working with custom apps, and giving analysts the right data at the right moment.
What makes Mate different from other AI SOC solutions?
Three things set Mate apart: instant organizational context, works with any tool, and keeps getting smarter. Most AI SOC tools start blank and need weeks to tune. Mate learns your organization in hours, including its tools, policies, and context. It connects to everything analysts use, from legacy systems to scripts, portals, and Excel, and keeps learning from every investigation to become your organization’s brain.
Can Mate work in our unique, complex environment with our custom-built tools, scripts, and homegrown systems?
Yes. Mate works across your entire security ecosystem. Enterprise security spans years of configurations, from firewall rules and Terraform setups to custom apps and knowledge stored in wikis and SOPs. This knowledge lives everywhere, not just in your SIEM or EDR, and Mate works with all of it. The result is full coverage across your real environment and the accumulated wisdom behind it.
How can Mate deliver value on Day 1 if it hasn’t learned anything yet?
Most investigations start from zero, forcing analysts to rebuild context each time. Mate changes that. It instantly learns your organization by ingesting tickets, documentation, incidents, configurations, and behavior patterns in hours, not months. With full context from past investigations and decisions across teams, a “suspicious login from new geolocation” is resolved in seconds.
Does Mate only generate insights or can it also take actions?
Mate doesn’t just advise, it acts. It gathers evidence, correlates data, and as you build trust, can make decisions and close tickets with full documentation. For complex threats, it handles the manual work so analysts can focus on security thinking. You control the autonomy and keep oversight as trust builds. The result: simple cases resolved in seconds, complex ones in minutes.
Latio Security Operations AI Innovator 2026 badge round logo with black and white sections.

the consensus of masters

“Mate’s Security Context Graph enables environment-specific detection and response for more informed, accurate action.”

James Berthoty
James Berthoty