Mate security logo
the platform
WHAT IT DOES
OVERVIEW

Learn about the Mate Platform

AGENTIC THREAT HUNTING

Continuous, proactive and contextual hunts that look where it matters

AGENTIC DETECTION ENGINEERING

Detections written and tuned by agents, in context

Agentic INVESTIGATION

Full investigations run end to end by agents

Contextual INCIDENT RESPONSE

Response actions taken at agent speed

TECHNOLOGY
Technology
SECURITY CONTEXT GRAPH

Your environment, mapped for agents to reason over.

GAMEBOOKS

Mate’s answer to deterministic and brittle playbooks

Blogmate labs
Company
Company
About
Agents Village
Newsroom
Get a Demo
Get a Demo

The Agentic Defense Blog

Keep it real: defending through November’s chaos

November’s outages and attacks showed how hard it has become to tell a real attack from business as usual, and how costly a wrong call can be in either direction. Our CEO, Asaf Wiener, explains why teams now need AI to act on their behalf, and how deep context and CPR let those agents make the right call and take the right action in time.
Asaf Wiener
November 15, 2026

The New Normal: How to Defend Before You’re Certain

Oren Saban, Mate’s CPO, on why AI-driven attacks force teams to act before they know if they’re facing a bug, an outage or an intrusion. His practical guide shows how to get ready ahead of time: a tested safe mode you can flip in minutes, clear authority for people and agents to act alone, and the context to make sure the fast action is the right one.

Oren Saban
November 20, 2026

Data Collection and Data Cleaning: Where Accurate Security Agents Start

For twenty years, security operations ran on a simple process. Send every log you can afford to one place, write rules on top of it, and hire people to work the queue. The SIEM sat at the center, and everything else was arranged around it.

Mate Security
November 2, 2026

The A-Team: What Building AI Agents Taught Me About Building a Team

Asaf Wiener, CEO of the cyberdefense startup Mate, argues that the conditions that keep AI agents accurate at scale are the same ones that help people do their best work. He draws five lessons from building agents for enterprise security teams. Shared context builds a common culture. Clear structure lets people reason and move quickly. Compressing knowledge into playbooks helps the team keep the same standard as it grows. Leaders should filter out noise so teams know what matters. Onboarding should show how customers and patterns connect. His conclusion is that the people building agents deserve at least as much care as the agents’ environment gets.

Asaf Wiener
October 19, 2026

Accrued Accuracy: Building Trust in the Age of Agentic Cyberdefense

As AI takes on more cybersecurity tasks, accuracy becomes critical. Security agents must balance speed with safety to avoid disrupting business operations or missing real threats. Mate Security addresses this challenge with its CPR framework, which evaluates confidence, precision, and reversibility before allowing agents to act autonomously. Combined with Mate’s Security Context Graph, this approach aims to improve decision-making, reduce risk, and build trust in autonomous cyberdefense.

Asaf Wiener
October 18, 2026

Outsized impact: how to build a winning team

When Mate was named one of LinkedIn’s Top Startups, the first question I asked myself was: what actually makes a company grow? A great product, the right market, strong technology, good timing and execution all matter. But I work on the people side of Mate every day, and from where I sit, the answer is people.

Mika Shtrowise
October 14, 2026

Life After SOAR (Hint - It's Not Next-Gen SOAR)

SOAR is now one capability within agentic cyber defense. Before renewing your SOAR license in 2026, see why playbooks break on change and what migrating to an agentic platform involves.

Inbal Argov
October 4, 2026

PEAK Threat Hunting Framework: How to Turn Hunt Findings Into Detections That Compound Over Time

Learn how the PEAK Threat Hunting Framework turns one-off hunts into a compounding security program, using its 3 phases, 3 hunt types, and a direct path from findings to detections. This article also breaks down what makes PEAK different from earlier frameworks and how it maps to Continuous Detection / Continuous Response.

Sharon Rosenman
September 18, 2026

Outpace the Frontier

As AI accelerates cyberattacks, defenders must match their speed with controlled, trustworthy AI rather than slowing defensive innovation and adoption.

Asaf Wiener
September 15, 2026

Claude Mythos and the New Threat Landscape for SOC: What It Means for Defenders and How to Respond

Claude Mythos signals a new era of AI-augmented cyberattacks. This guide explains what it is, how it changes the threat landscape for SOC teams, and the investigation strategies and best practices defenders need to respond effectively.

Sharon Rosenman
August 31, 2026

Gamebooks let security teams control their AI agents without wrecking accuracy or coverage

Deterministic about intent, dynamic about execution - so your team customizes the investigation without breaking the AI underneath.

Inbal Argov
August 27, 2026

How Context Knowledge Loss Breaks Cloud Incident Response Programs at Scale

Cloud incident response demands different tools, playbooks, and expertise than traditional IR, especially as attackers move from access to exfiltration within minutes and shared-responsibility models create investigation blind spots. Learn how context knowledge loss quietly breaks cloud incident response programs at scale, and what it takes to build one that gets stronger, not weaker, with every analyst who comes and goes.

Sharon Rosenman
August 18, 2026

AI SOC Agents: What They Do, How They Work, and What Sets the Best Apart

Not all AI SOC Agents investigate with the same accuracy. This article explains how they work, the core capabilities and types that define mature platforms, and why grounding every investigation in an organization's real assets and institutional knowledge is what separates reliable security decisions from generic automation.

Sharon Rosenman
August 13, 2026

AI Changed Security Operations. Mate Proved It.

Following Mate’s Series A, CEO Asaf Wiener shares the vision behind the company and why security operations need a new AI-native foundation.
Asaf Wiener
July 30, 2026

Top 6 AI Threat Detection Tools for Modern SOC Teams in 2026

Learn how the 6 best AI threat detection tools compare for enterprise SOC teams in 2026. This article breaks them down by the job each does: endpoint, network, SIEM, and AI SOC analyst, then walks through five practical criteria to help you match the right tool to the gaps in your stack.

Sharon Rosenman
July 24, 2026

Agentic SOC: How AI Agents Are Transforming Security Operations

Learn how agentic SOC platforms use AI agents to investigate every alert end to end, cut response times from hours to minutes, and ground every decision in your organization's own context instead of generic rules.

Sharon Rosenman
July 21, 2026

Incident Response Checklist: Steps, Templates, and Best Practices

Learn how to build an incident response checklist that helps security teams detect, contain, investigate, and recover from threats without missing critical steps. Explore checklist types, core components, common challenges, and best practices for improving response speed, consistency, and operational readiness.

Sharon Rosenman
July 7, 2026

AI SOC Automation: How Context-Driven Investigations Transform Security Operations

Most AI SOC deployments stall because they automate alerts without understanding organizational context. Learn how AI SOC automation works, the architectures and workflows behind it, the metrics that measure its effectiveness, and how it integrates with SIEM, SOAR, EDR, and threat intelligence platforms.

Sharon Rosenman
July 6, 2026

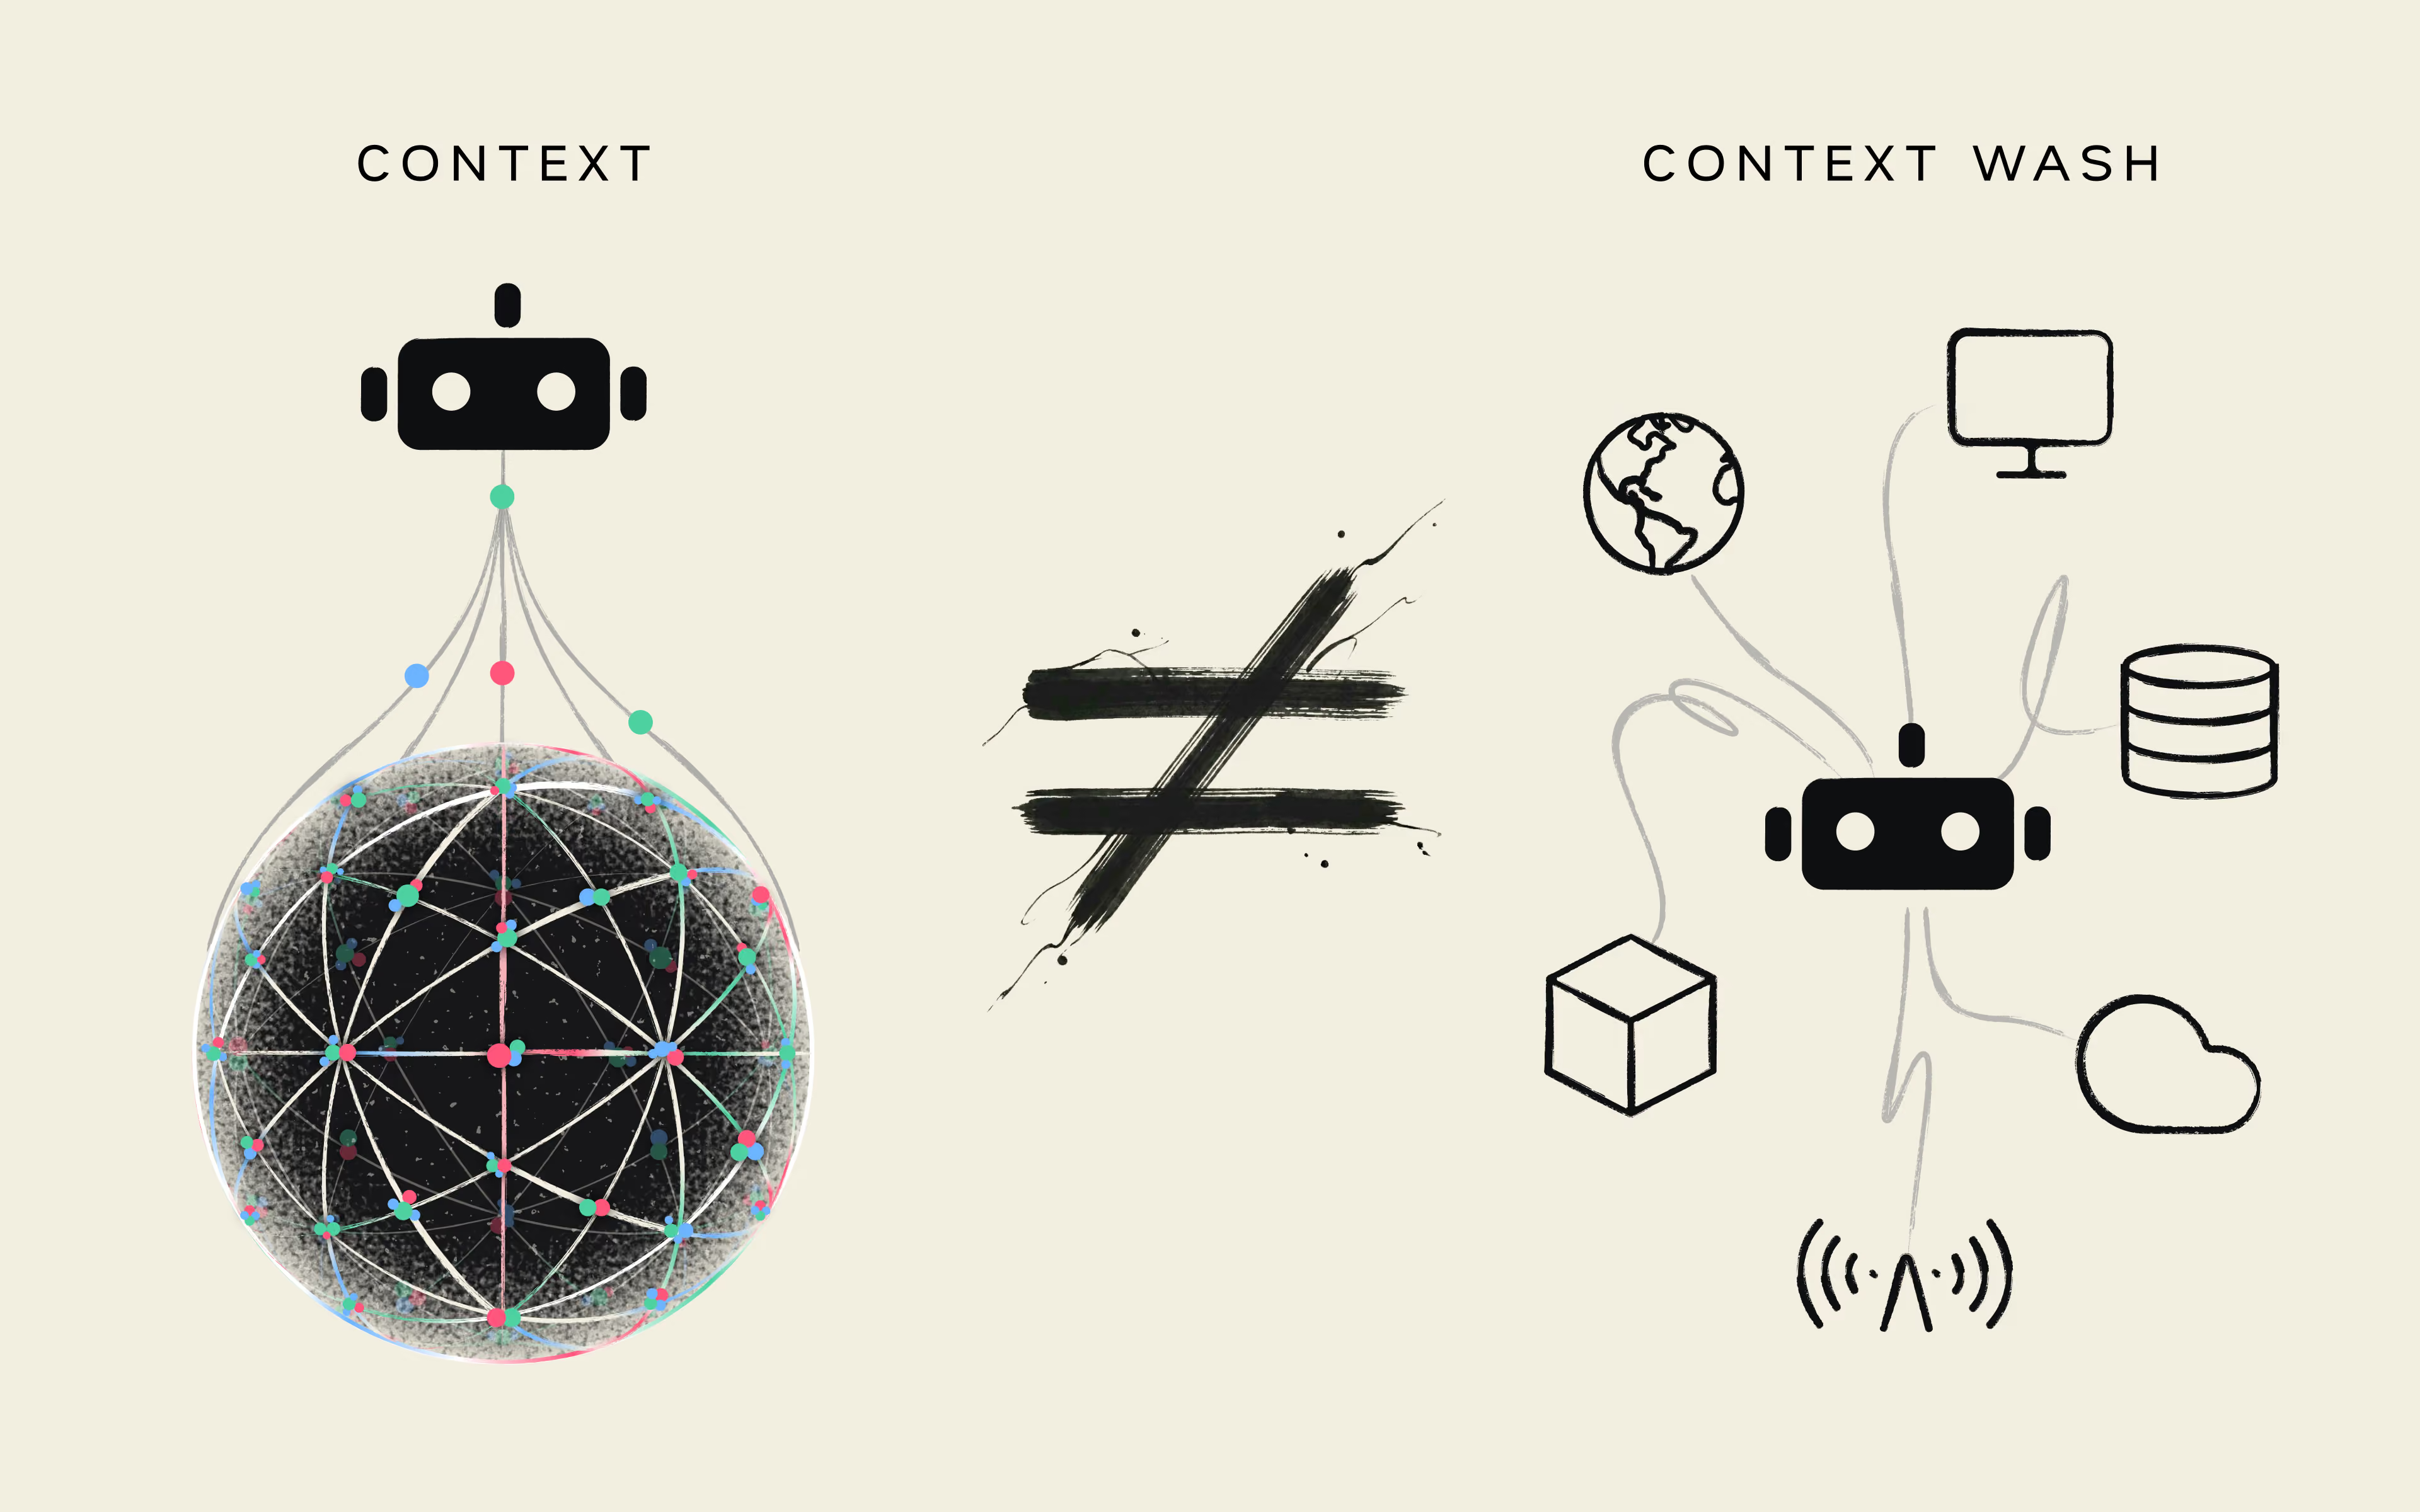
Context Wash - How AI SOC Vendors Hollowed Out Their Strongest Word

You will hear "context” from every AI SOC vendor. Here's a five-question rubric to tell which ones actually have it, before you write the check.

Zach Christensen
June 30, 2026

How to Measure and Maximize AI SOC ROI Across Modern Security Operations

AI SOC ROI measures the return security teams get from automating triage, investigation, and response, across analyst efficiency, breach cost avoidance, and detection speed. Learn how to measure it with a clear calculation framework, build a leadership-ready business case, and track the metrics that prove value over time.

Sharon Rosenman
June 17, 2026

Top 8 SOC Tools for Enterprise Security Operations in 2026

SOC platforms help security teams reduce alert fatigue, improve investigation efficiency, and scale operations with AI-driven workflows, XDR integration, automated response, and cloud-native detection. Learn how modern SOCs cut false positives, streamline triage, and accelerate threat response with context-aware automation.

Sharon Rosenman
June 4, 2026

You can't out-respond the volume. Try CD/CR

The math of defense breaks before Mythos-class capabilities go mainstream. Here's the architecture that survives - and four questions to test if you've built it.

Oren Saban
May 21, 2026

Continuous Detection / Continuous Response - a new Security Operations Framework

Asaf Wiener
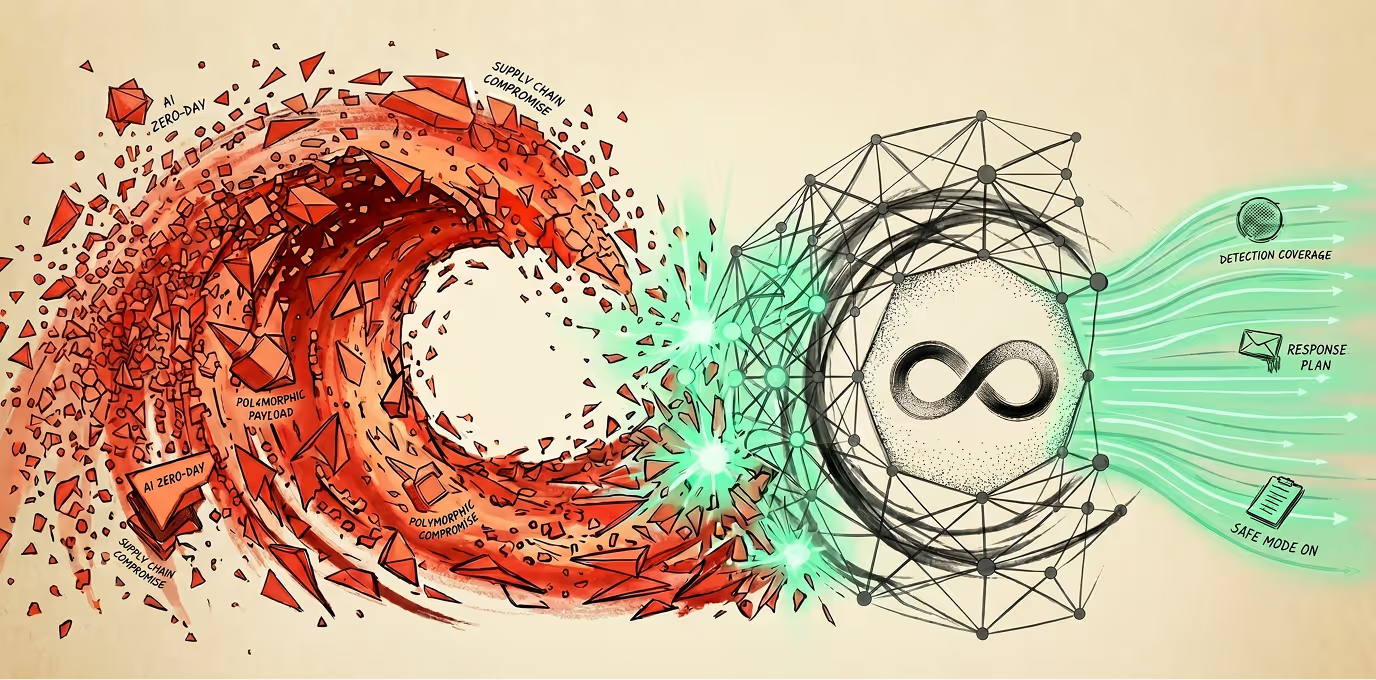
May 18, 2026

AI is the New C2 for Supply Chain Attacks

An analysis of modern CI/CD supply chain attacks, revealing how AI-generated variants bypass IOC-based detection and scale mass exploitation.

Yuval Skitel
May 14, 2026

Detection Engineering: How to Reduce Alert Noise & Improve SOC Performance

Detection engineering helps SOC teams cut alert noise, improve threat detection accuracy, and scale security operations through continuous tuning, contextual enrichment, and automated investigations. Learn how modern teams reduce false positives, map detections to MITRE ATT&CK, and accelerate response with AI-driven workflows.

Sharon Rosenman
May 13, 2026

AI SOC: How It Works, Key Benefits & What to Look For

AI SOCs fail without organizational context, leading to generic investigations, false positives, and inconsistent decisions. Learn how Mate Security uses a Security Context Graph to add institutional memory, contextual reasoning, and continuous learning for faster, more accurate, and transparent SOC investigations.

Sharon Rosenman
May 12, 2026

Mate’s Guide to Investigating the Axios Supply Chain Attack

A real-world walkthrough of an Axios supply chain attack, showing how Mate’s AI agents detected, investigated, and contained threats in a CI/CD environment before impact.

Dana Rozen
April 5, 2026

Why We Built the Security Context Graph

Why AI SOC agents fail, and how Mate fixes it. Learn how the Security Context Graph adds context, memory, and reasoning to deliver accurate, consistent investigations.

Oren Saban
February 19, 2026

Introducing: the Security Context Graph

An introduction to the Security Context Graph, Mate’s data model that gives AI SOC agents real context, improving accuracy, consistency, and trust in investigations.

Asaf Wiener
February 19, 2026

Mate Security Now Available on AWS Marketplace

Mate Security is now available on AWS Marketplace, enabling faster procurement and deployment of its AI SOC platform while delivering measurable improvements in efficiency and response times.

Mate Security
January 15, 2026

Mate Security Selected for the 2026 CrowdStrike, AWS & NVIDIA Cybersecurity Startup Accelerator

Mate Security joins the 2026 CrowdStrike, AWS & NVIDIA accelerator to advance AI-powered SOC innovation and scale next-generation cloud security solutions.

Mate Security
January 5, 2026

A Simulated Attack Story on React Server Components to Exploit React2Shell

A simulated React2Shell attack from a SOC perspective, revealing early weak signals, exploitation, and how RCE unfolds in real environments, plus detection and prevention insights.

Mate Research Team
December 22, 2025

npm Chalk & Debug Packages Compromised: How to Check If You're Impacted

18 popular npm packages were compromised to hijack crypto transactions. Learn how to detect exposure, secure CI/CD pipelines, and quickly remediate affected dependencies.

Oren Saban
December 10, 2025

Things I Learned About Security From SOCcer

What SOCs can learn from elite soccer teams: coordination wins. Discover how better tool integration, shared context, and teamwork can reduce noise and improve security outcomes.

Oren Saban
December 10, 2025

Keep AI on the Leash

Why autonomous SOCs fail, and how to fix it. Learn why human-AI collaboration, not full automation, leads to better detection, smarter investigations, and stronger security outcomes.

Asaf Wiener
December 10, 2025

Make FPs an Asset Instead of a Time Waste

Turn false positives into an advantage. Learn how antifragile SOCs use benign alerts, missed threats, and recurring incidents to continuously improve detection and stay ahead of evolving threats.

Oren Saban
December 10, 2025

Swiss Cheese Security: How Detection Tuning Creates Vulnerabilities

Detection exclusions create hidden security gaps. Learn how static exceptions lead to “Swiss cheese” defenses, and why dynamic context is key to reducing noise without increasing risk.

Oren Saban
December 1, 2025

The ROI of AI-Driven Security Automation: Metrics That Matter

AI automation makes old security metrics obsolete. The real ROI comes from beating attacker speed, stopping kill chains, detecting novel threats, and reducing business risk.

Asaf Wiener
December 1, 2025

See Mate in action

See how Mate transforms your data into context and uses it to investigate like a pro analyst.
Get a demo
Get a demo
Mate logo light

© 2026 mate security
All Rights Reserved  

contact
Privacy Policy
CCPA Notice
Trust Center
bug bounty program
partner deal registration
Hipaa compliant badgeMate security SOC 2 badgeMate security ISO badge

mate security All Rights Reserved  2026 Mate©