continuous
investigation
A world-class AI SOC platform that knows every detail of your environment, continuously adapts, and earns trust at every layer.


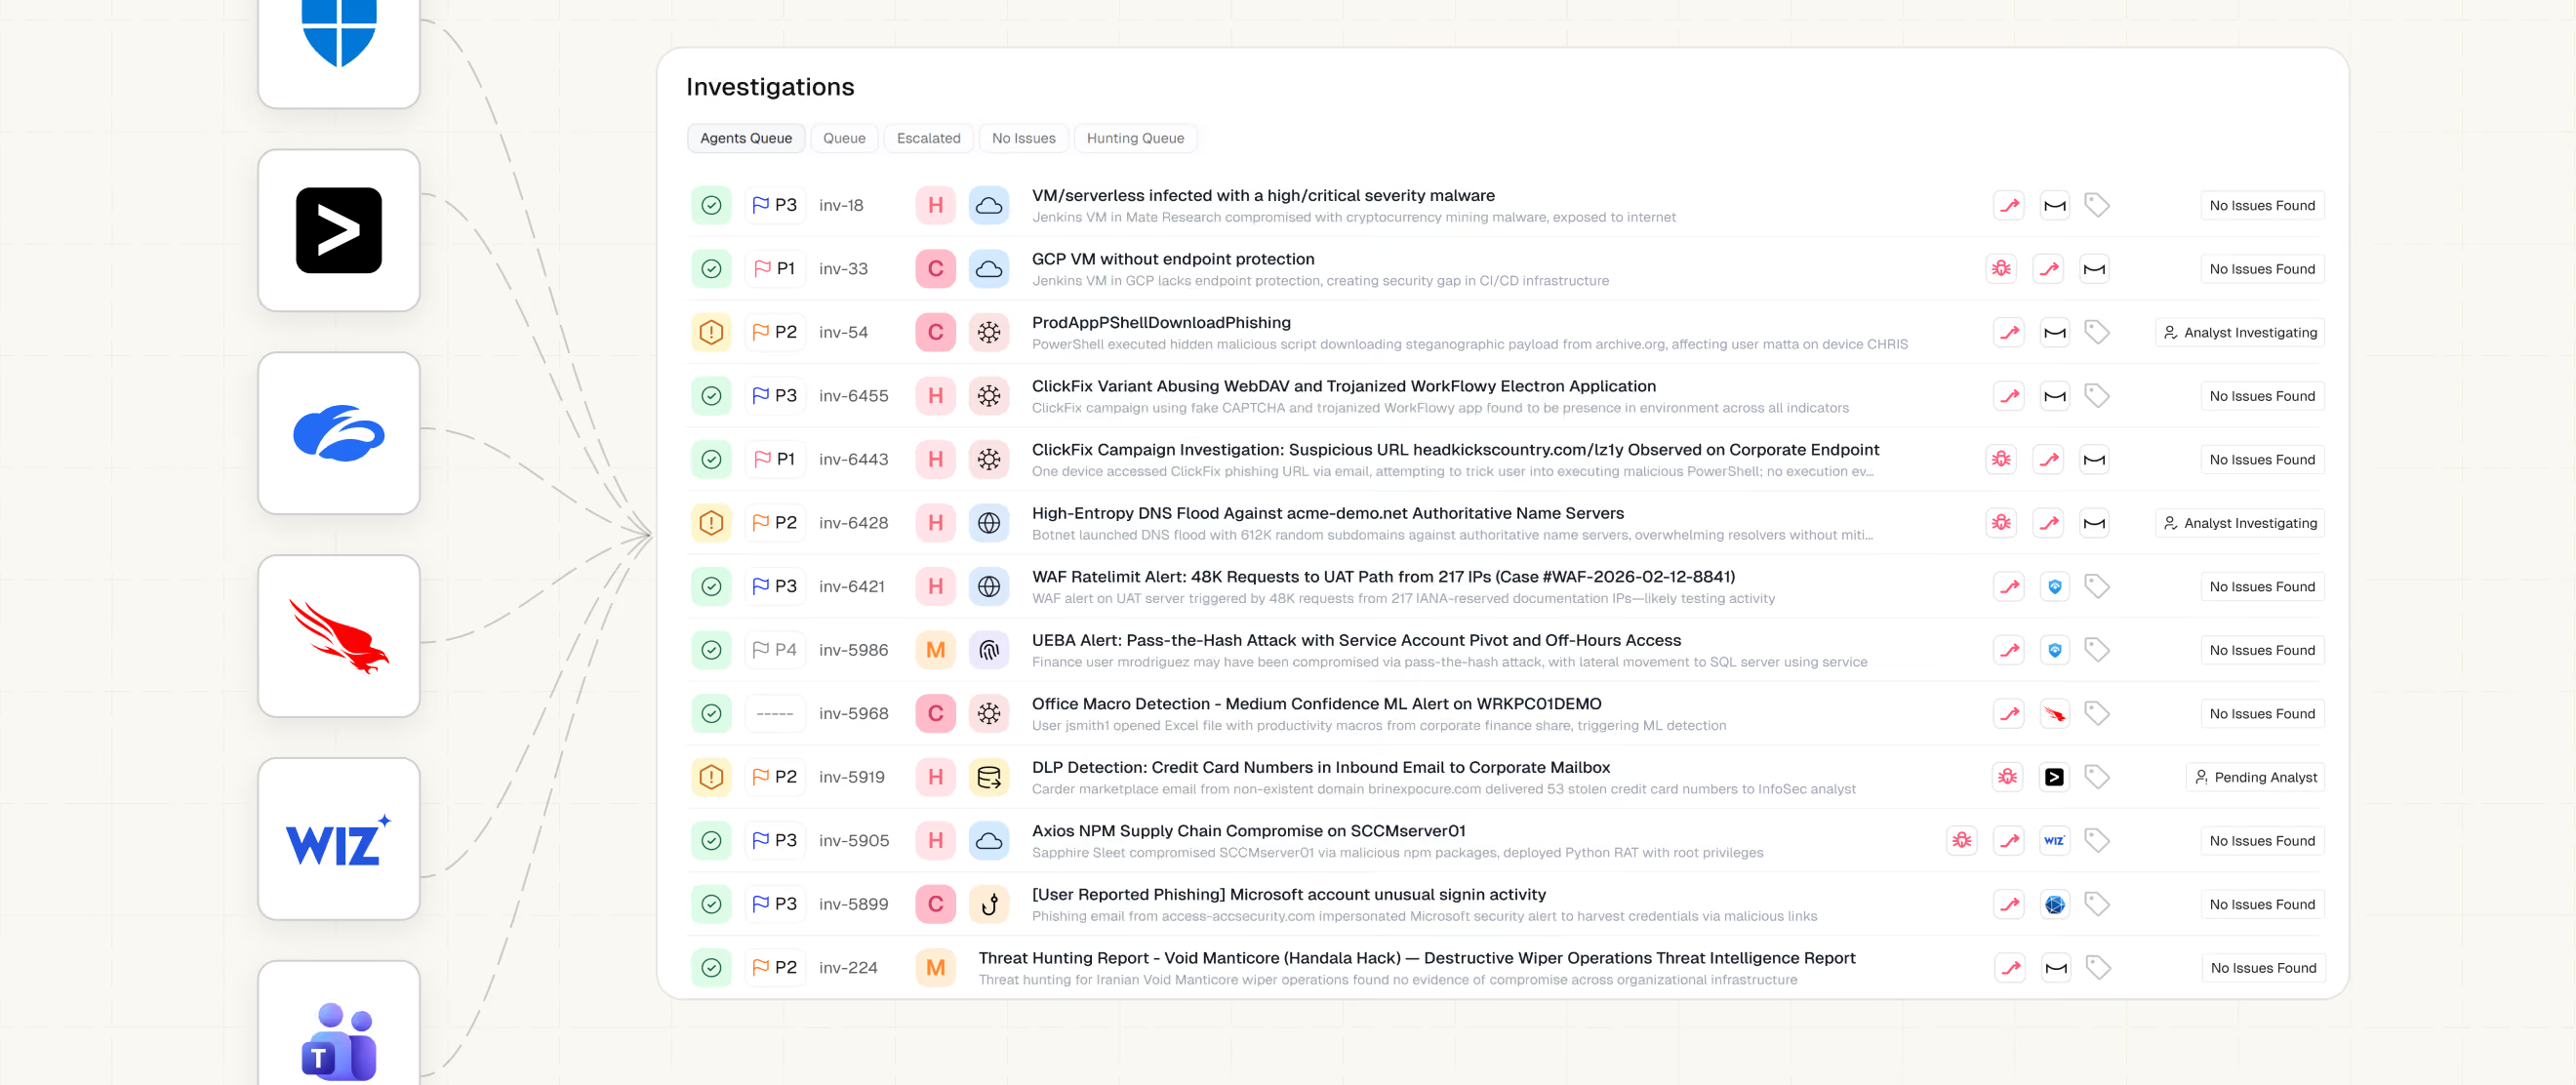
“Mate goes beyond processing alerts - it continuously learns how our environment operates. It becomes more attuned to what matters most, helping our team focus on the work that truly strengthens our security posture.”
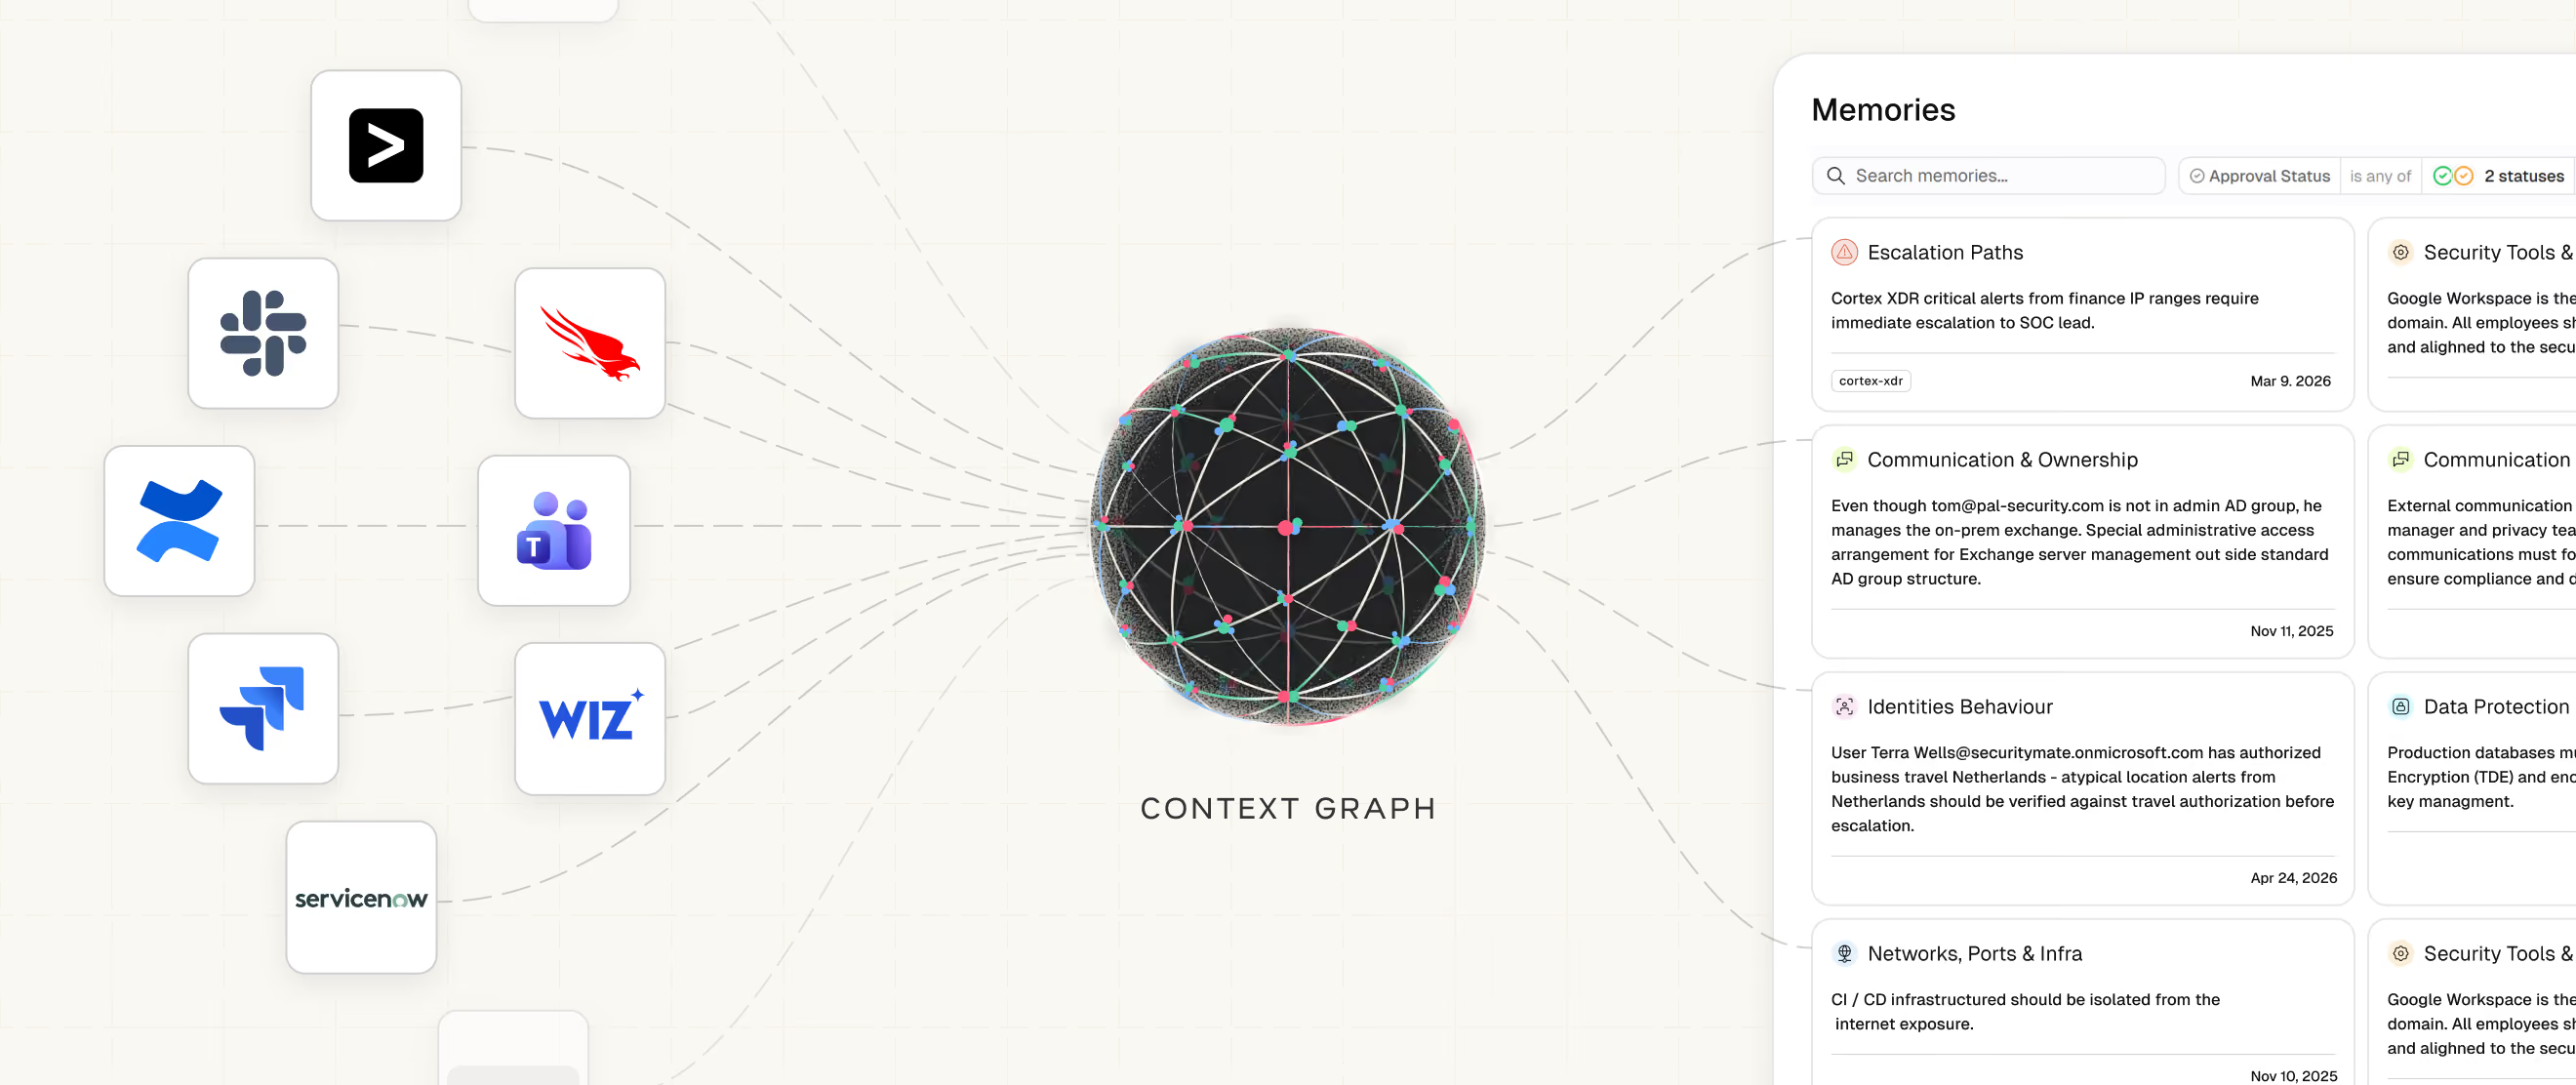
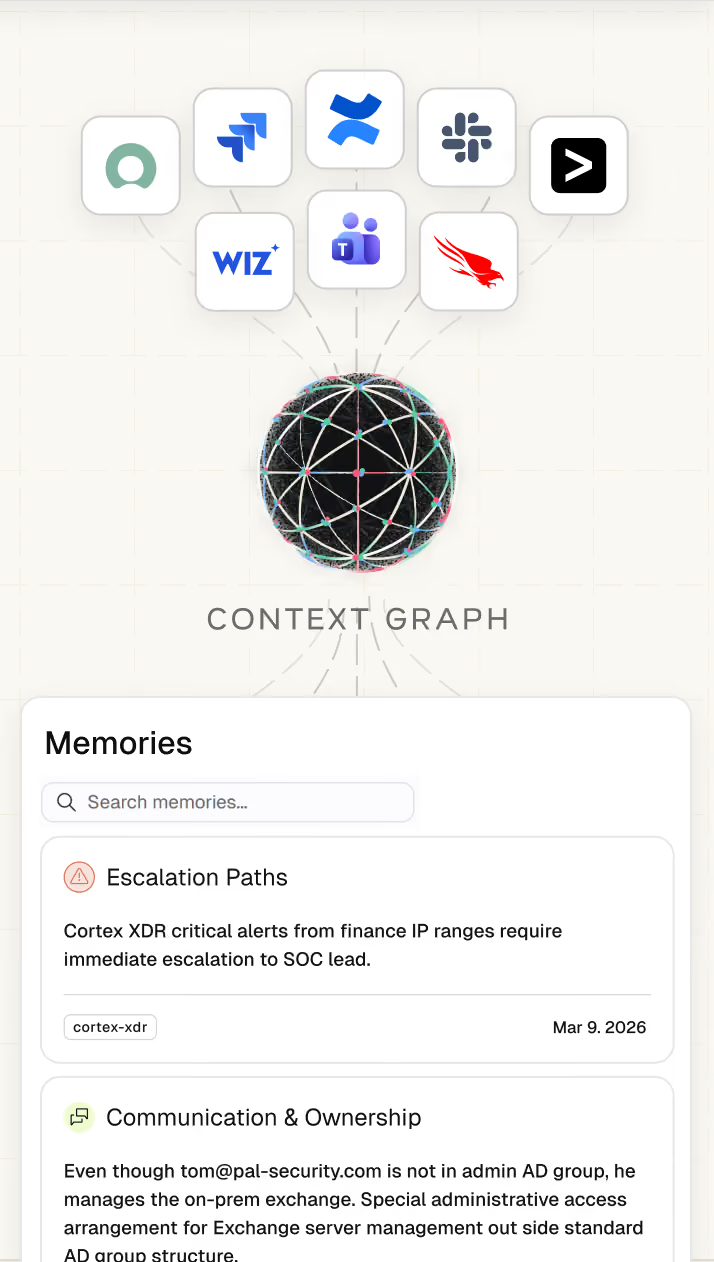
the security context graph
Mate captures the context your tools never recorded, then keeps it sourced, scored, and current.
Learn more →
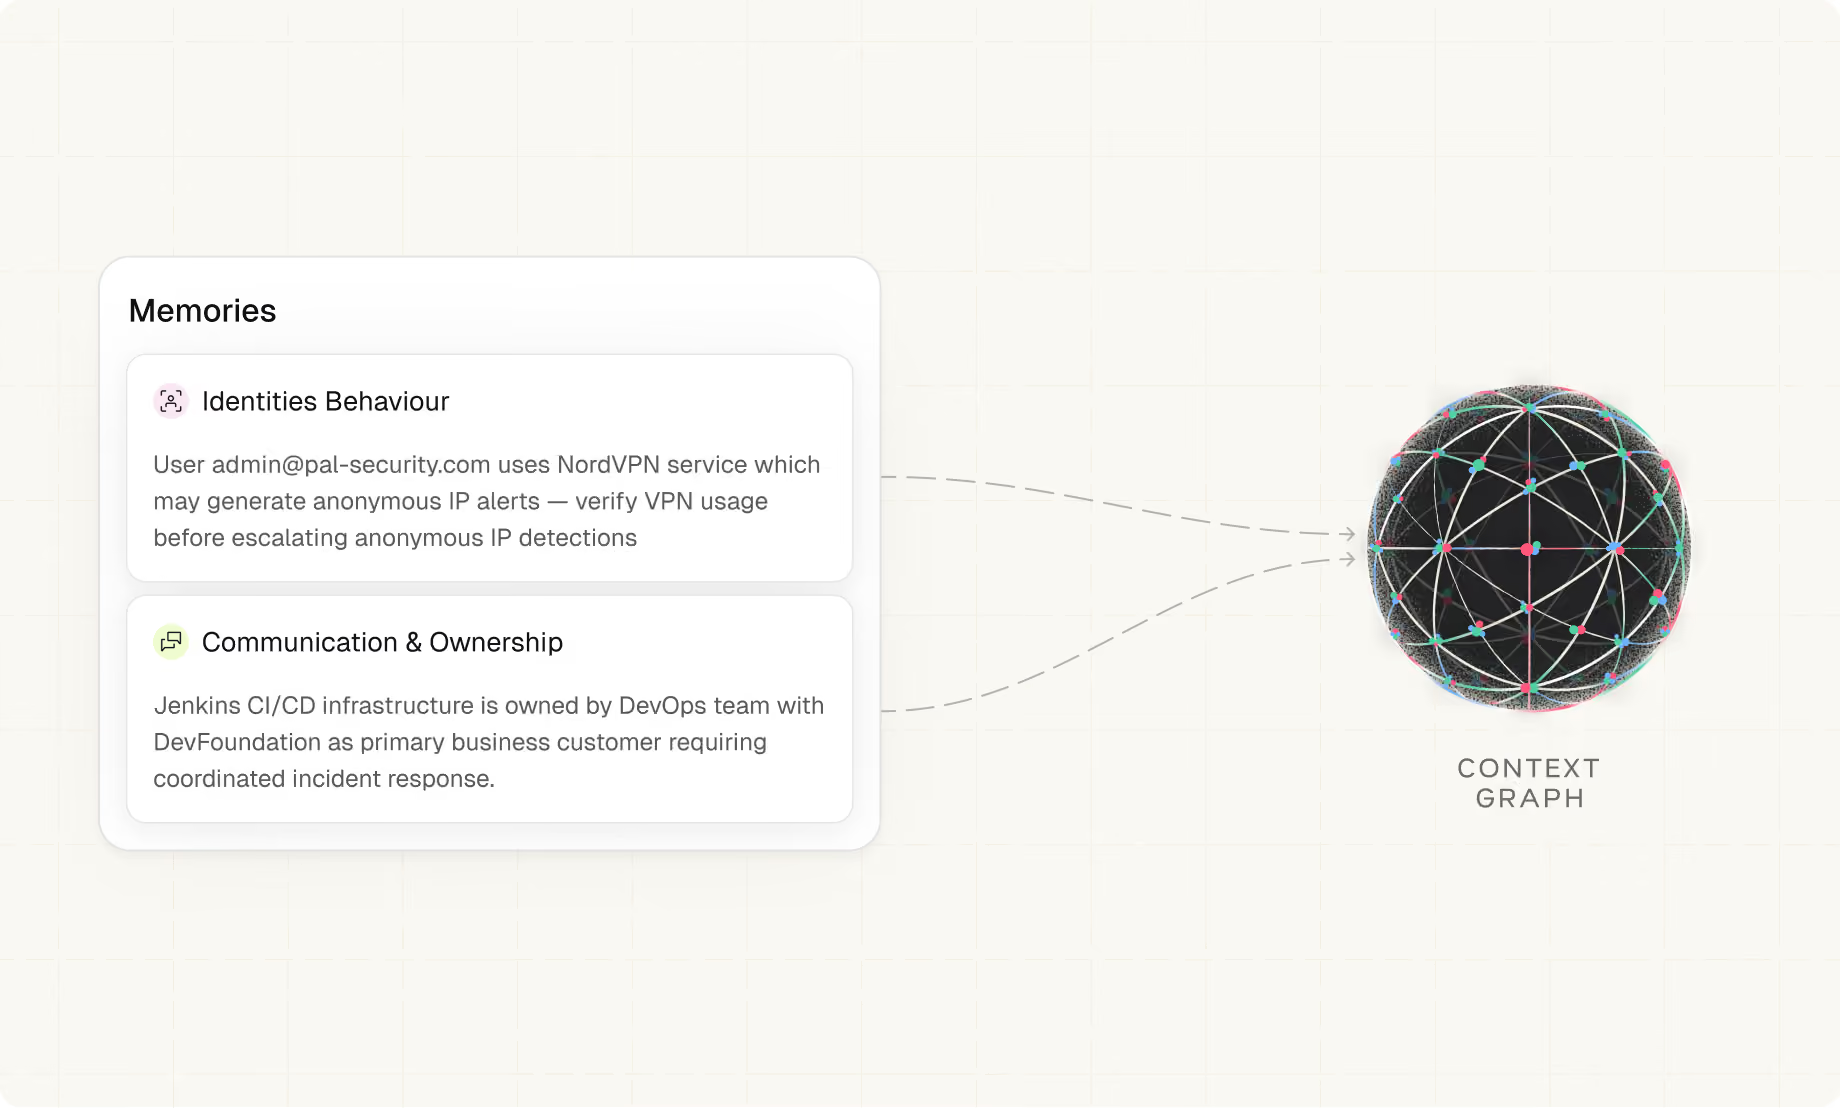
Memories
Every fact carries source, confidence, and freshness so agents know what to trust.

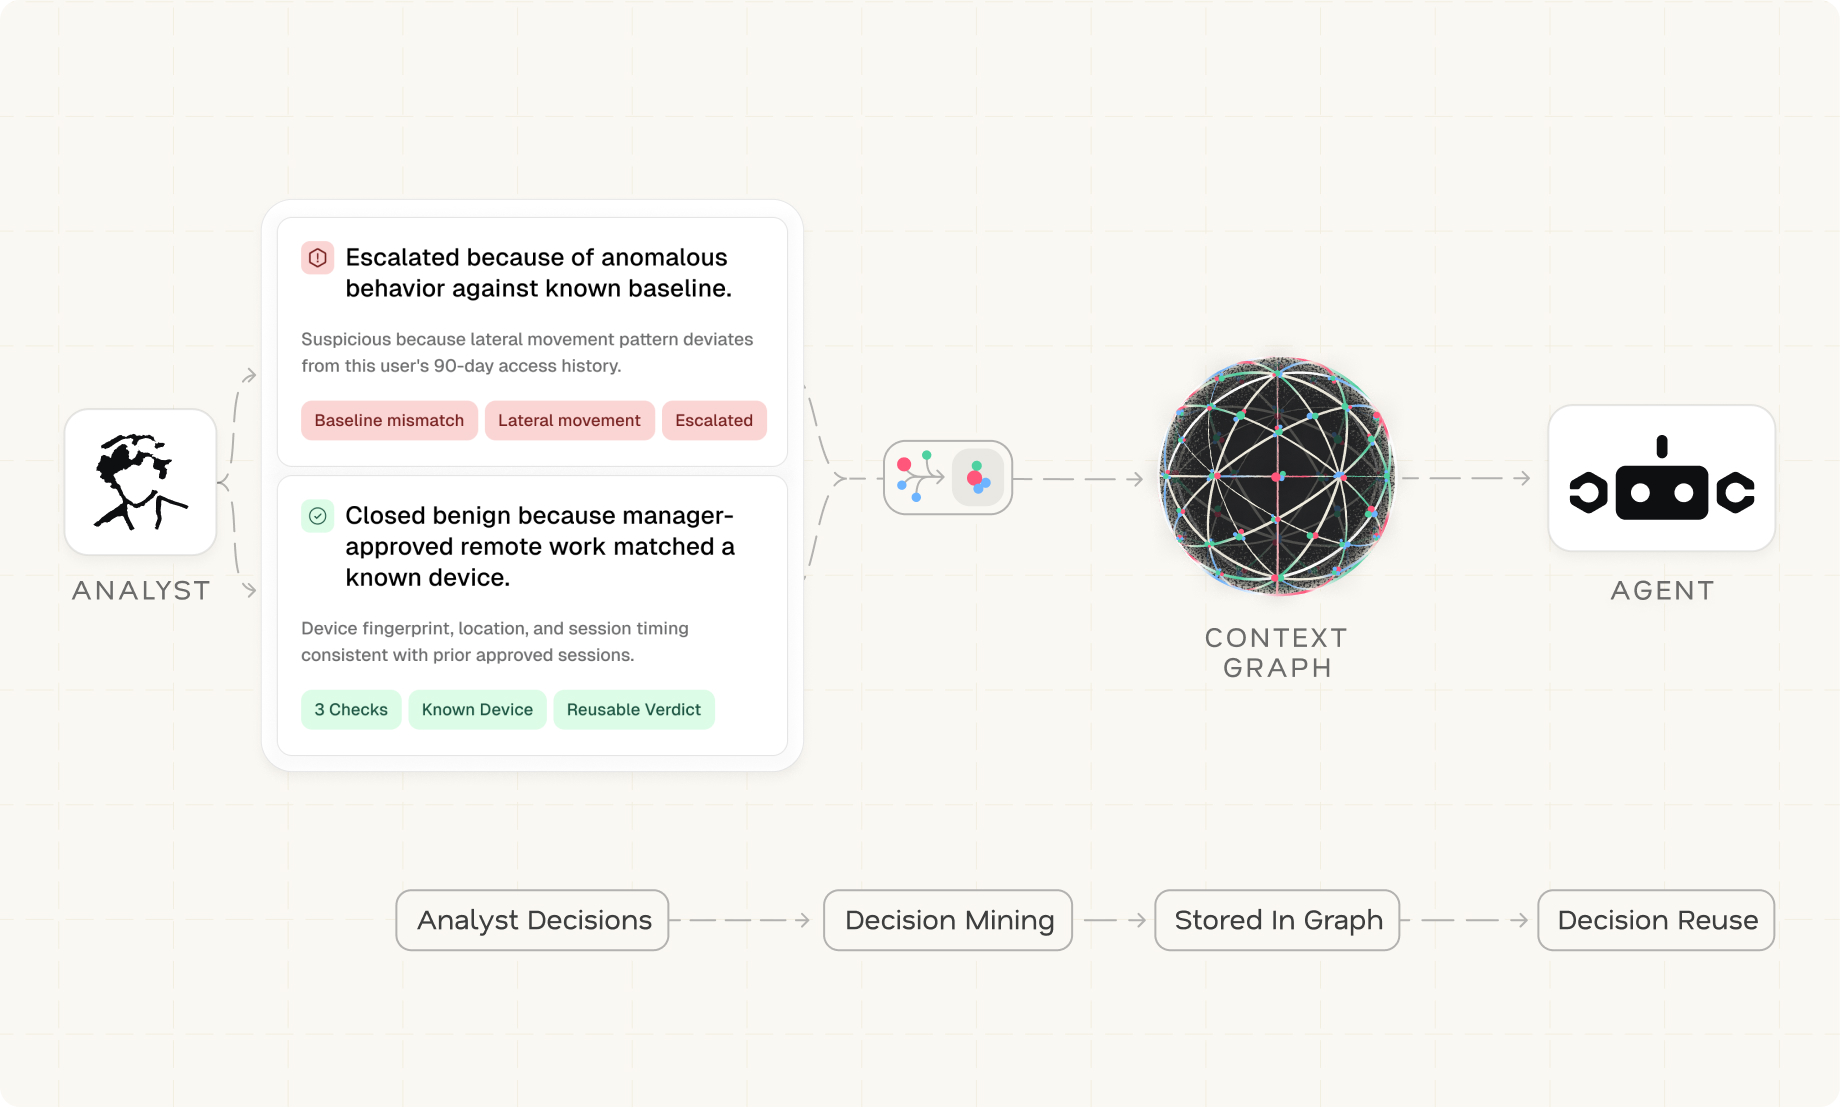
Decision Traces
Mate captures why an analyst made a call, not just the final verdict.

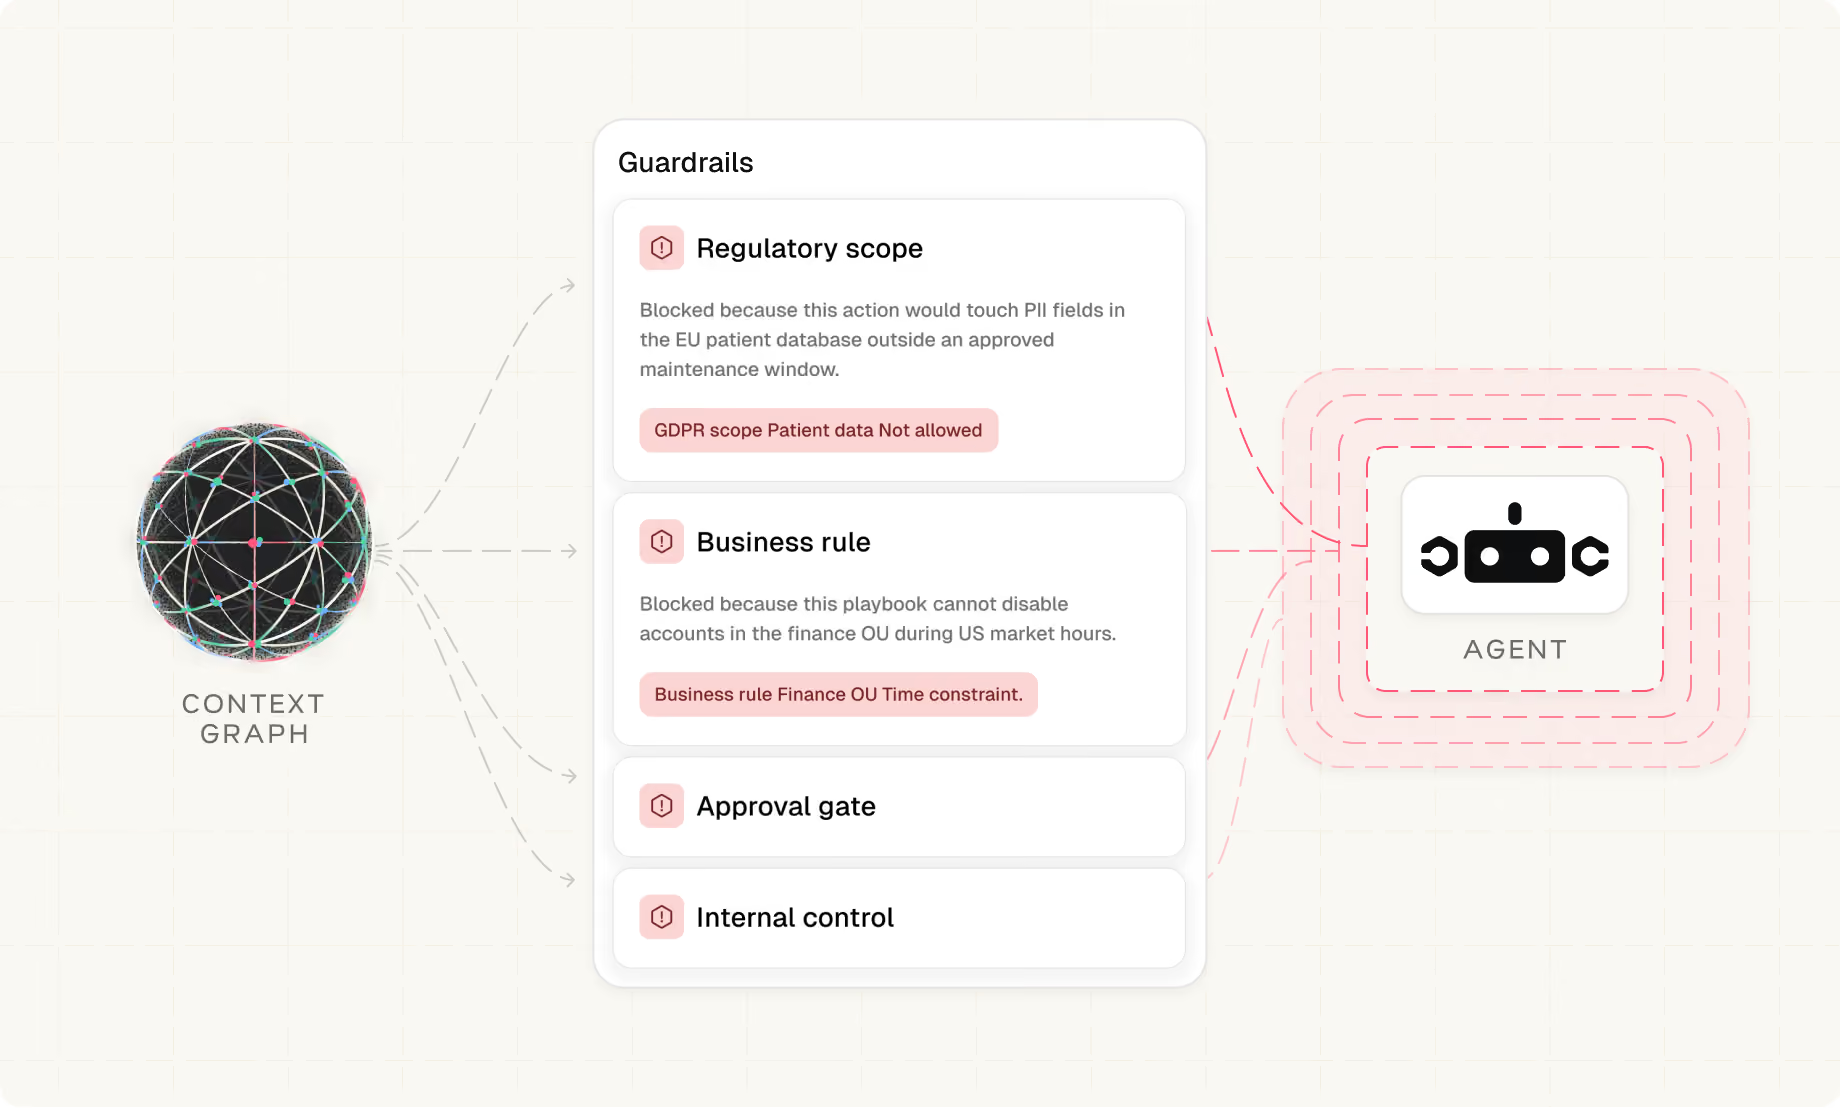
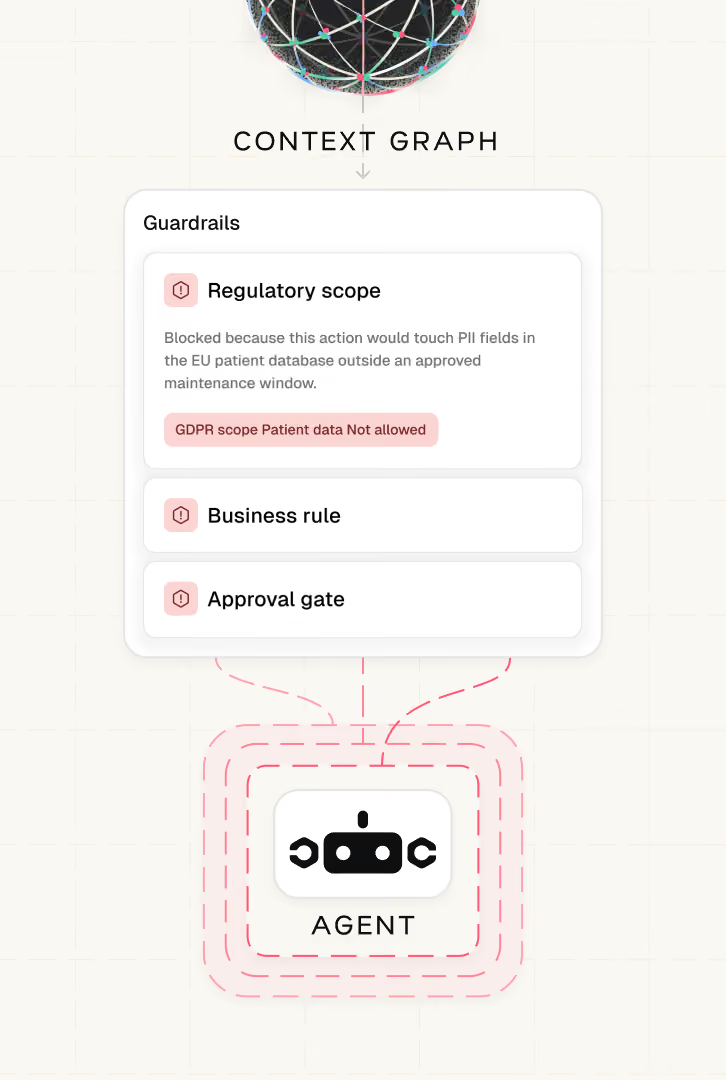
Guardrails
Knows when regulations, business rules, or internal controls constrain what an agent can do.

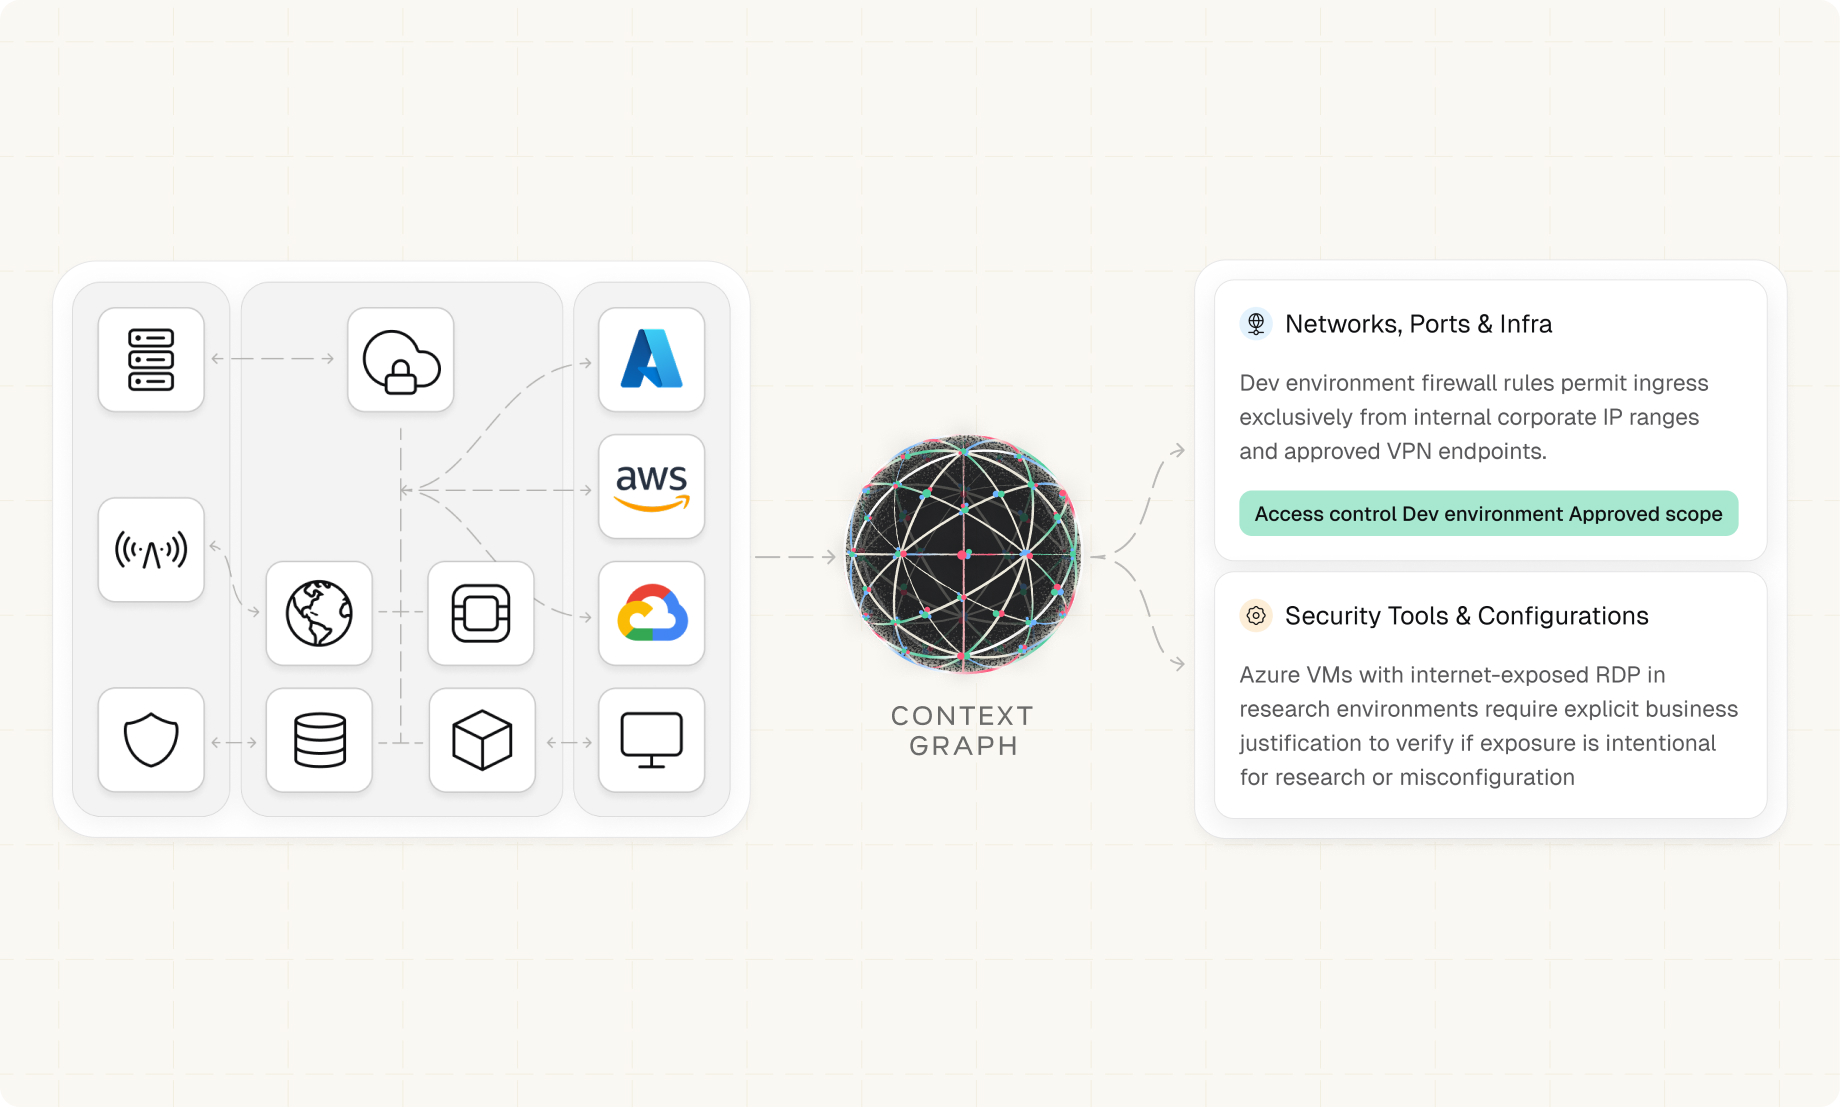
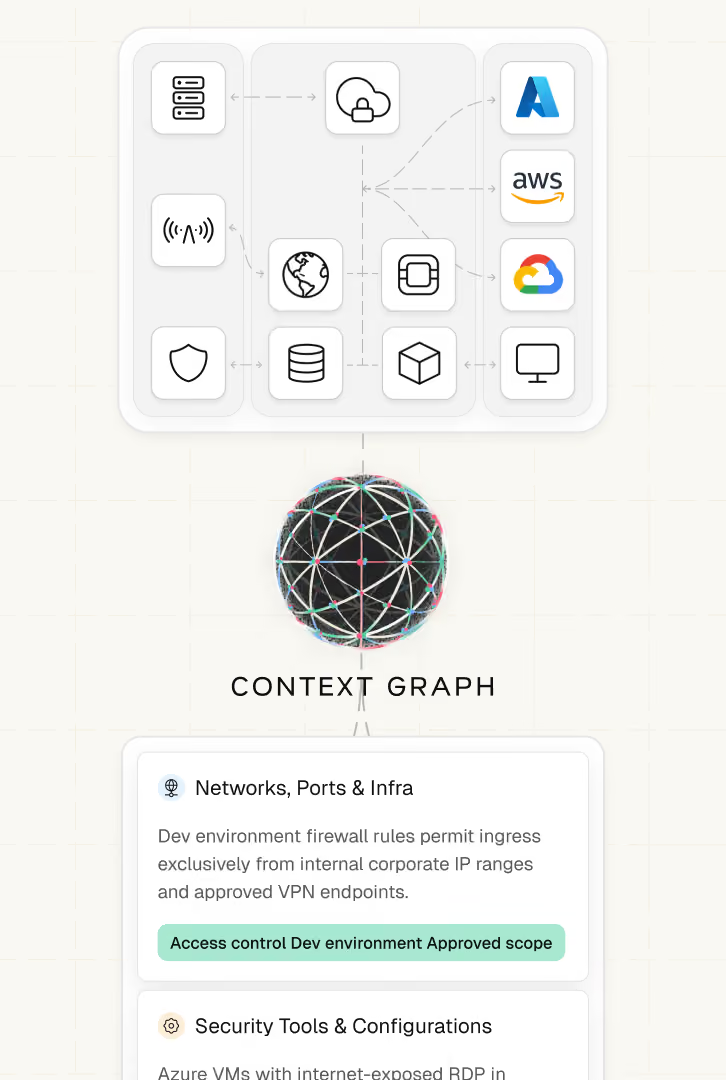
Architecture
Maps network topology and where each part of your security stack is deployed.
find threats before they find you
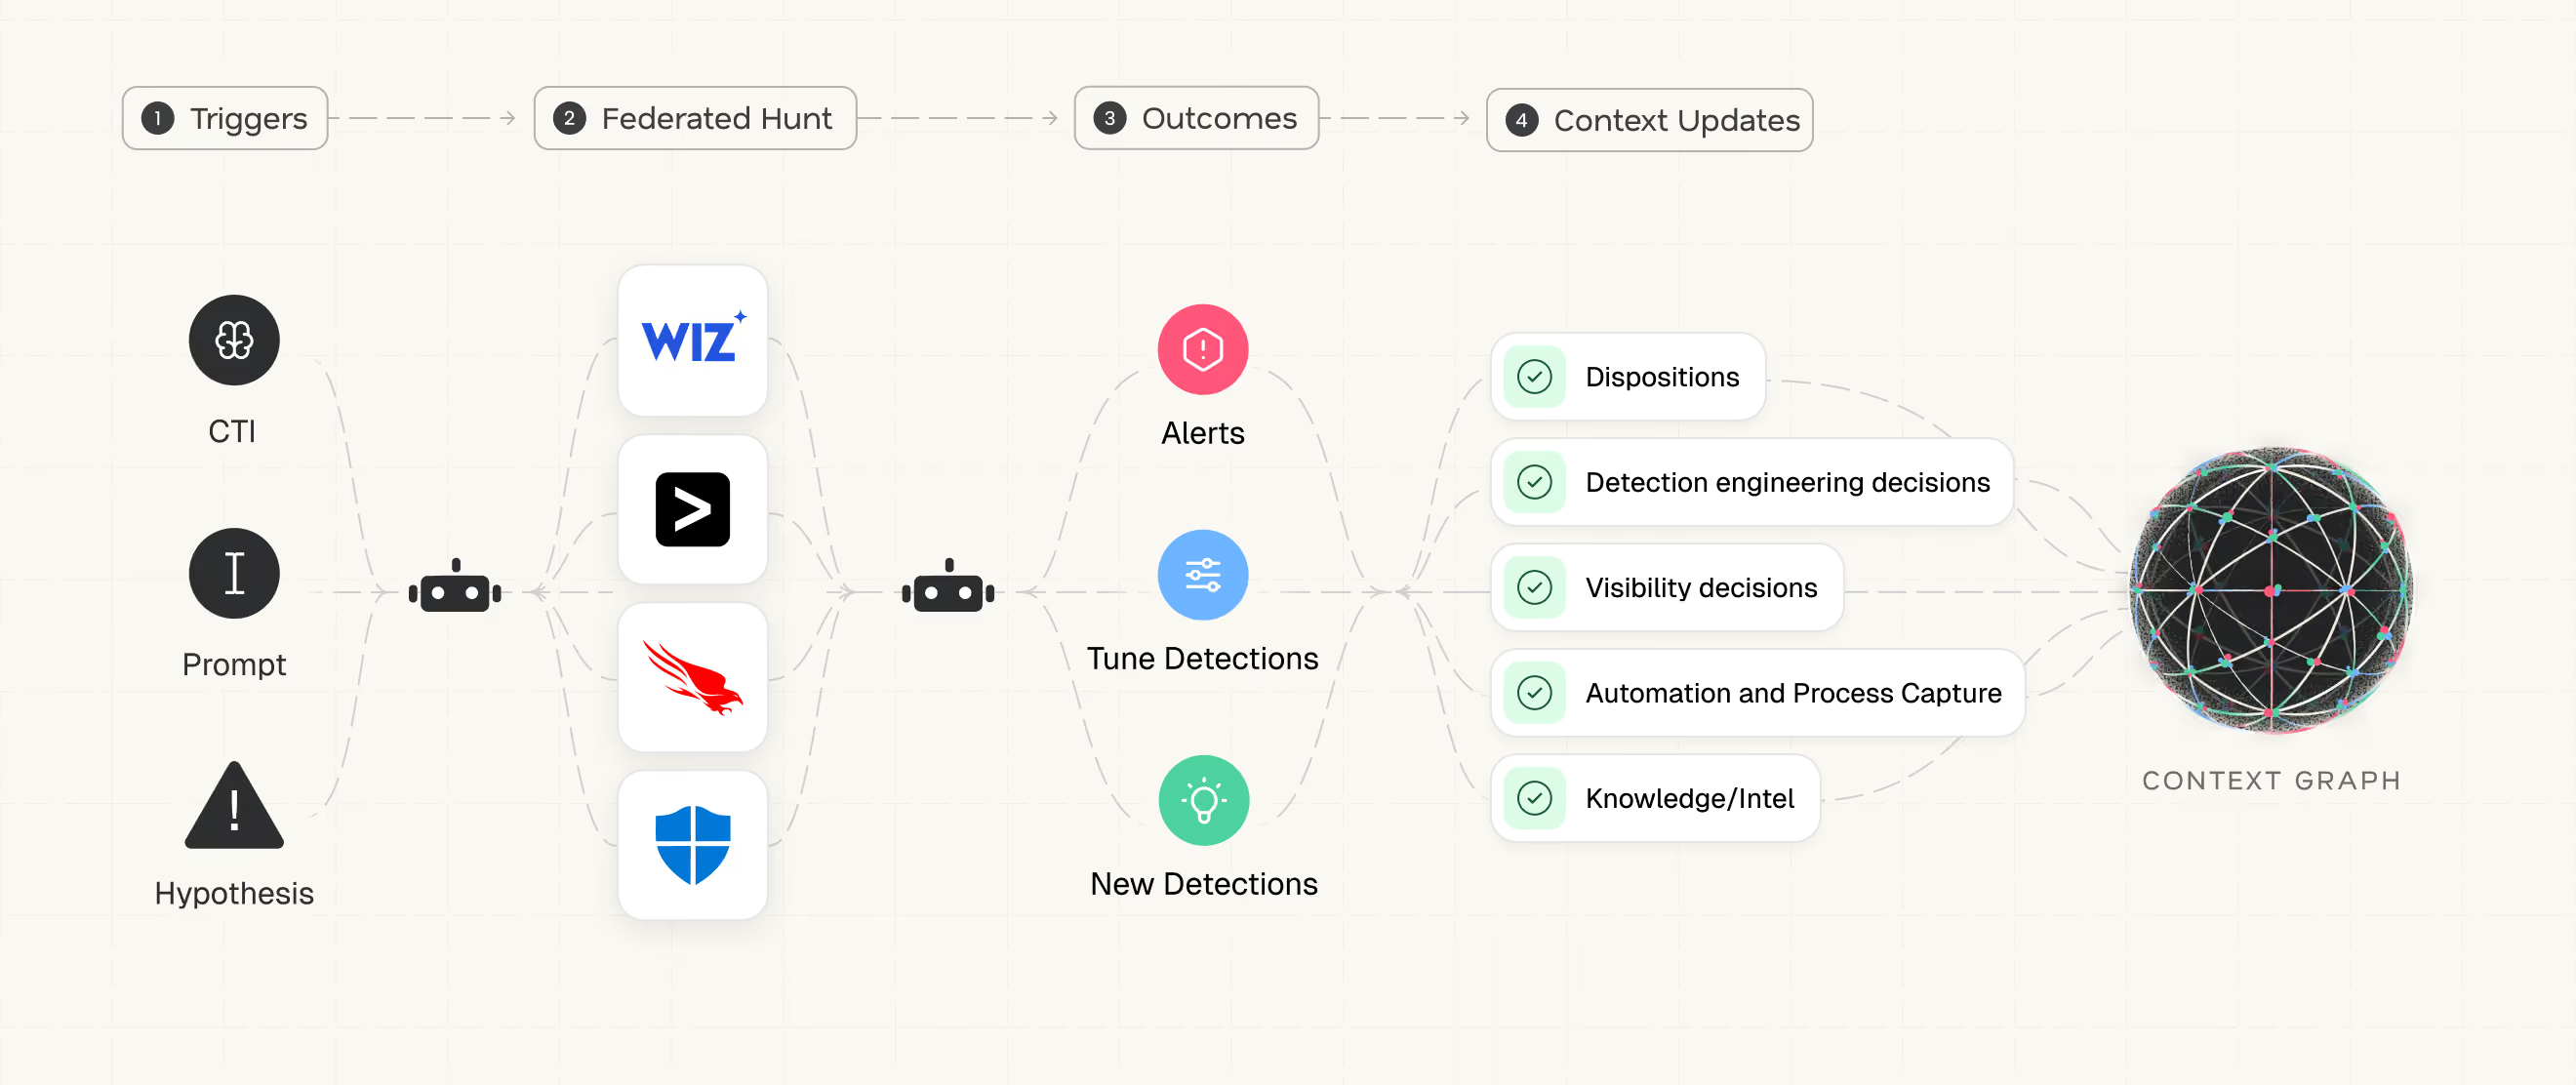
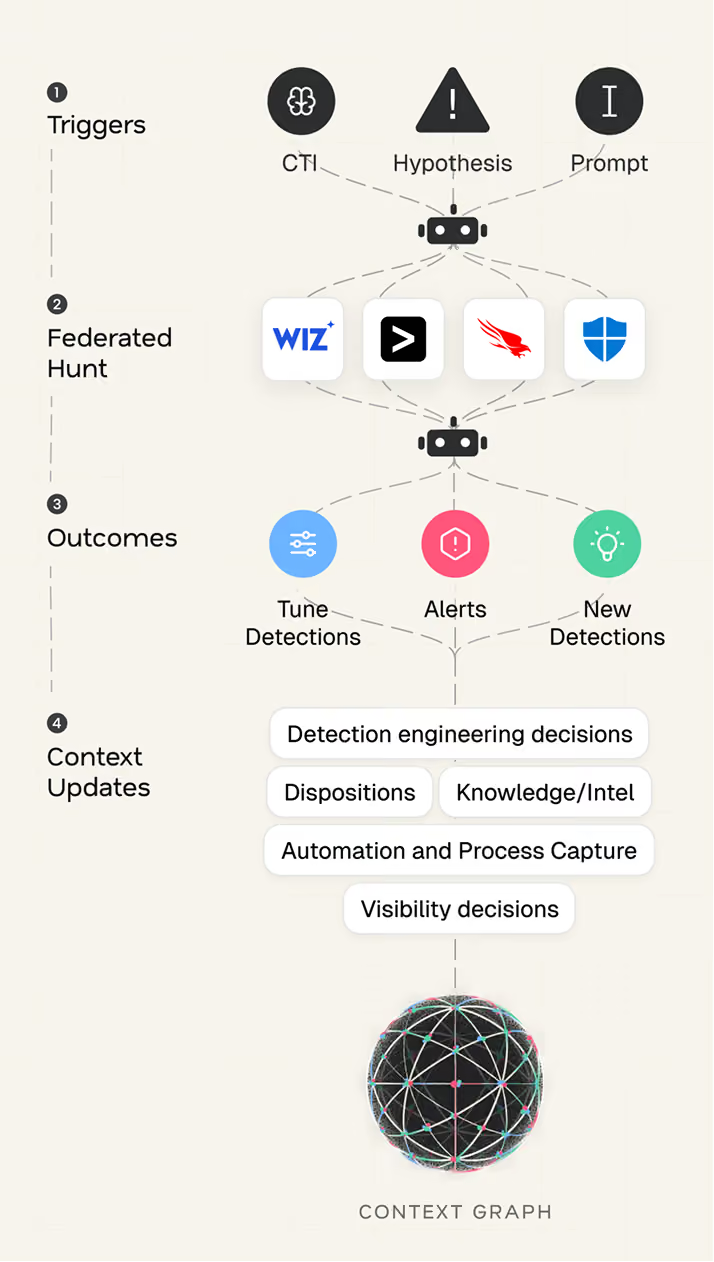
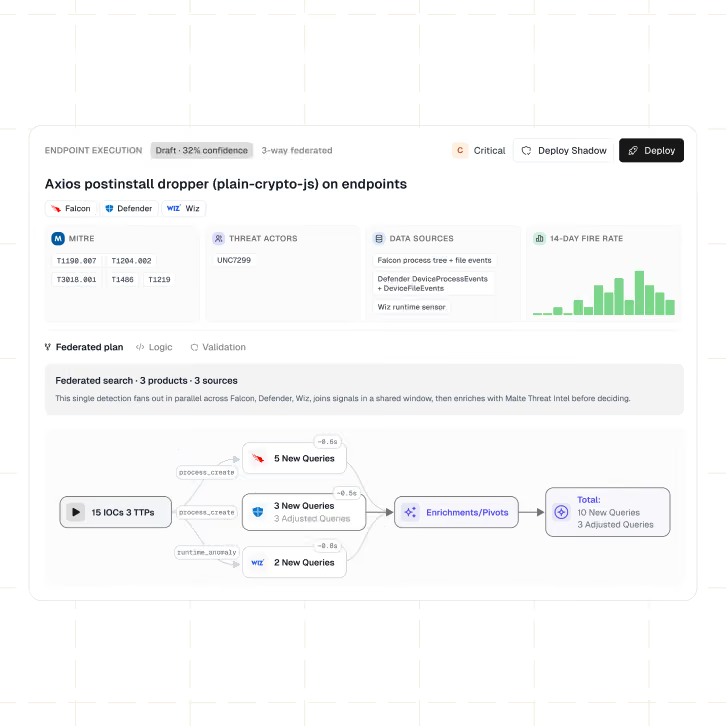
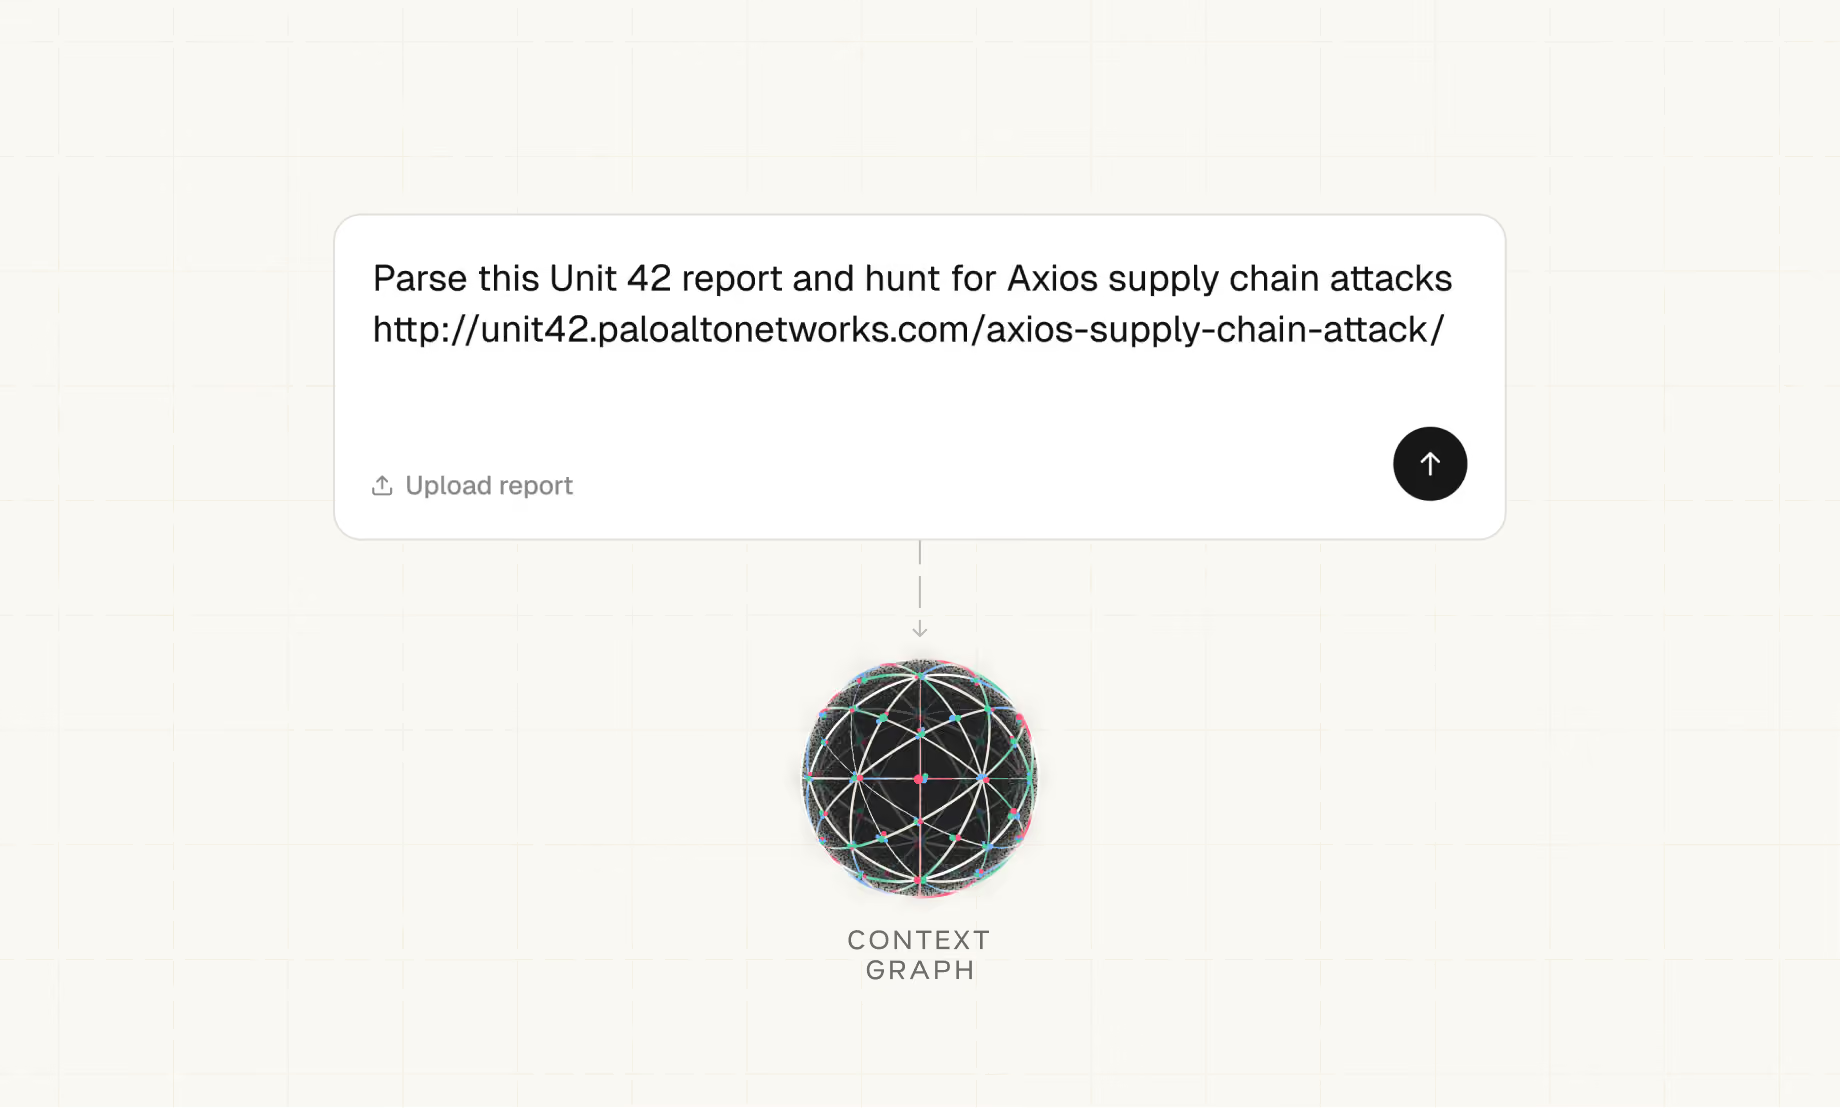
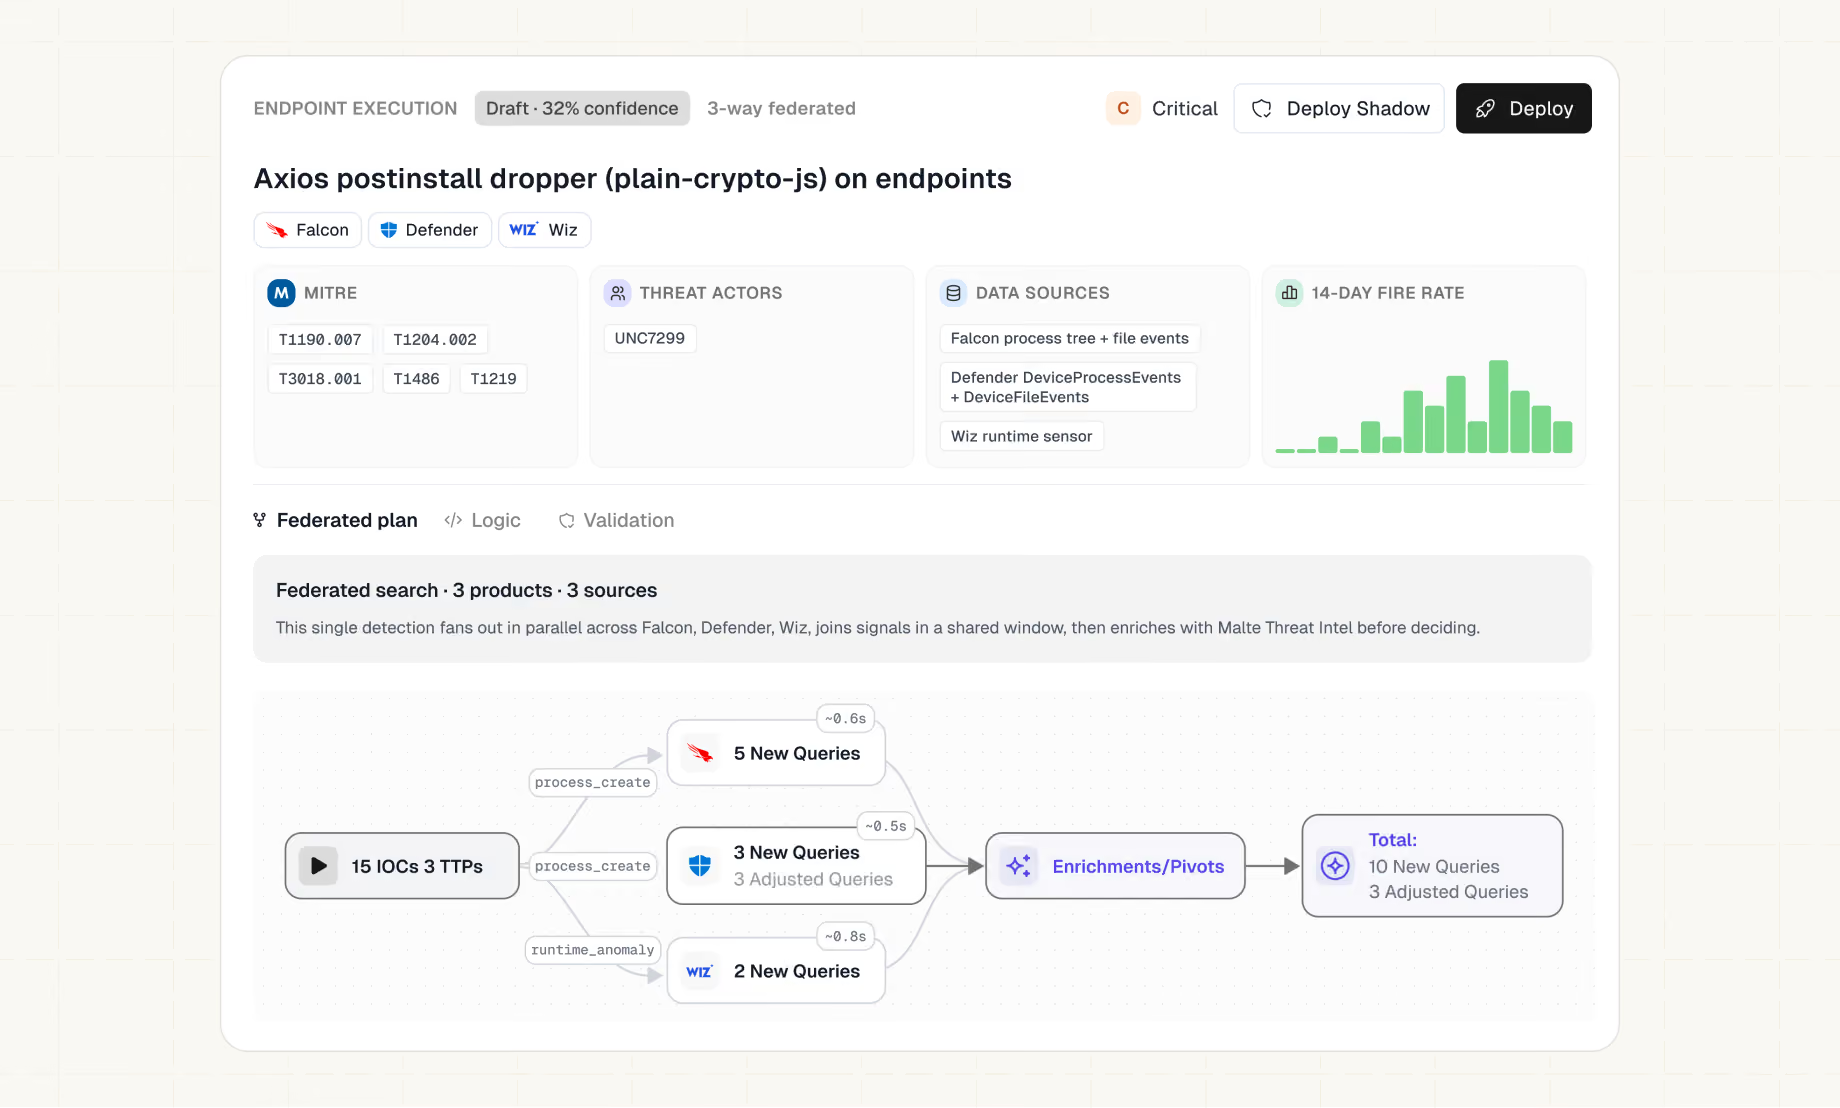
Paste a threat report or ask in plain language. Mate extracts IOCs and TTPs, then hunts across every connected tool.
Learn more →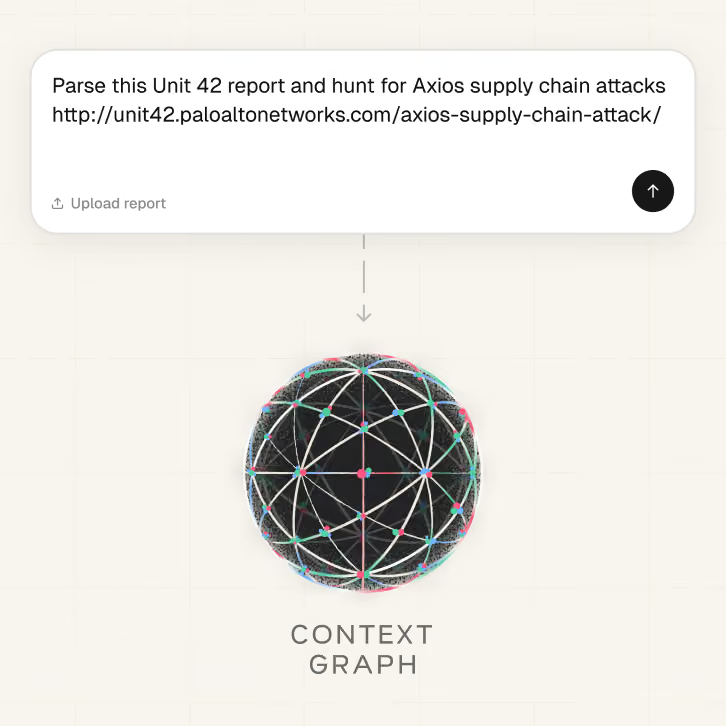
Expert-depth logic for every alert
Mate investigates every alert with the same depth your best analyst would bring, grounded in the context it already knows.
Learn more →
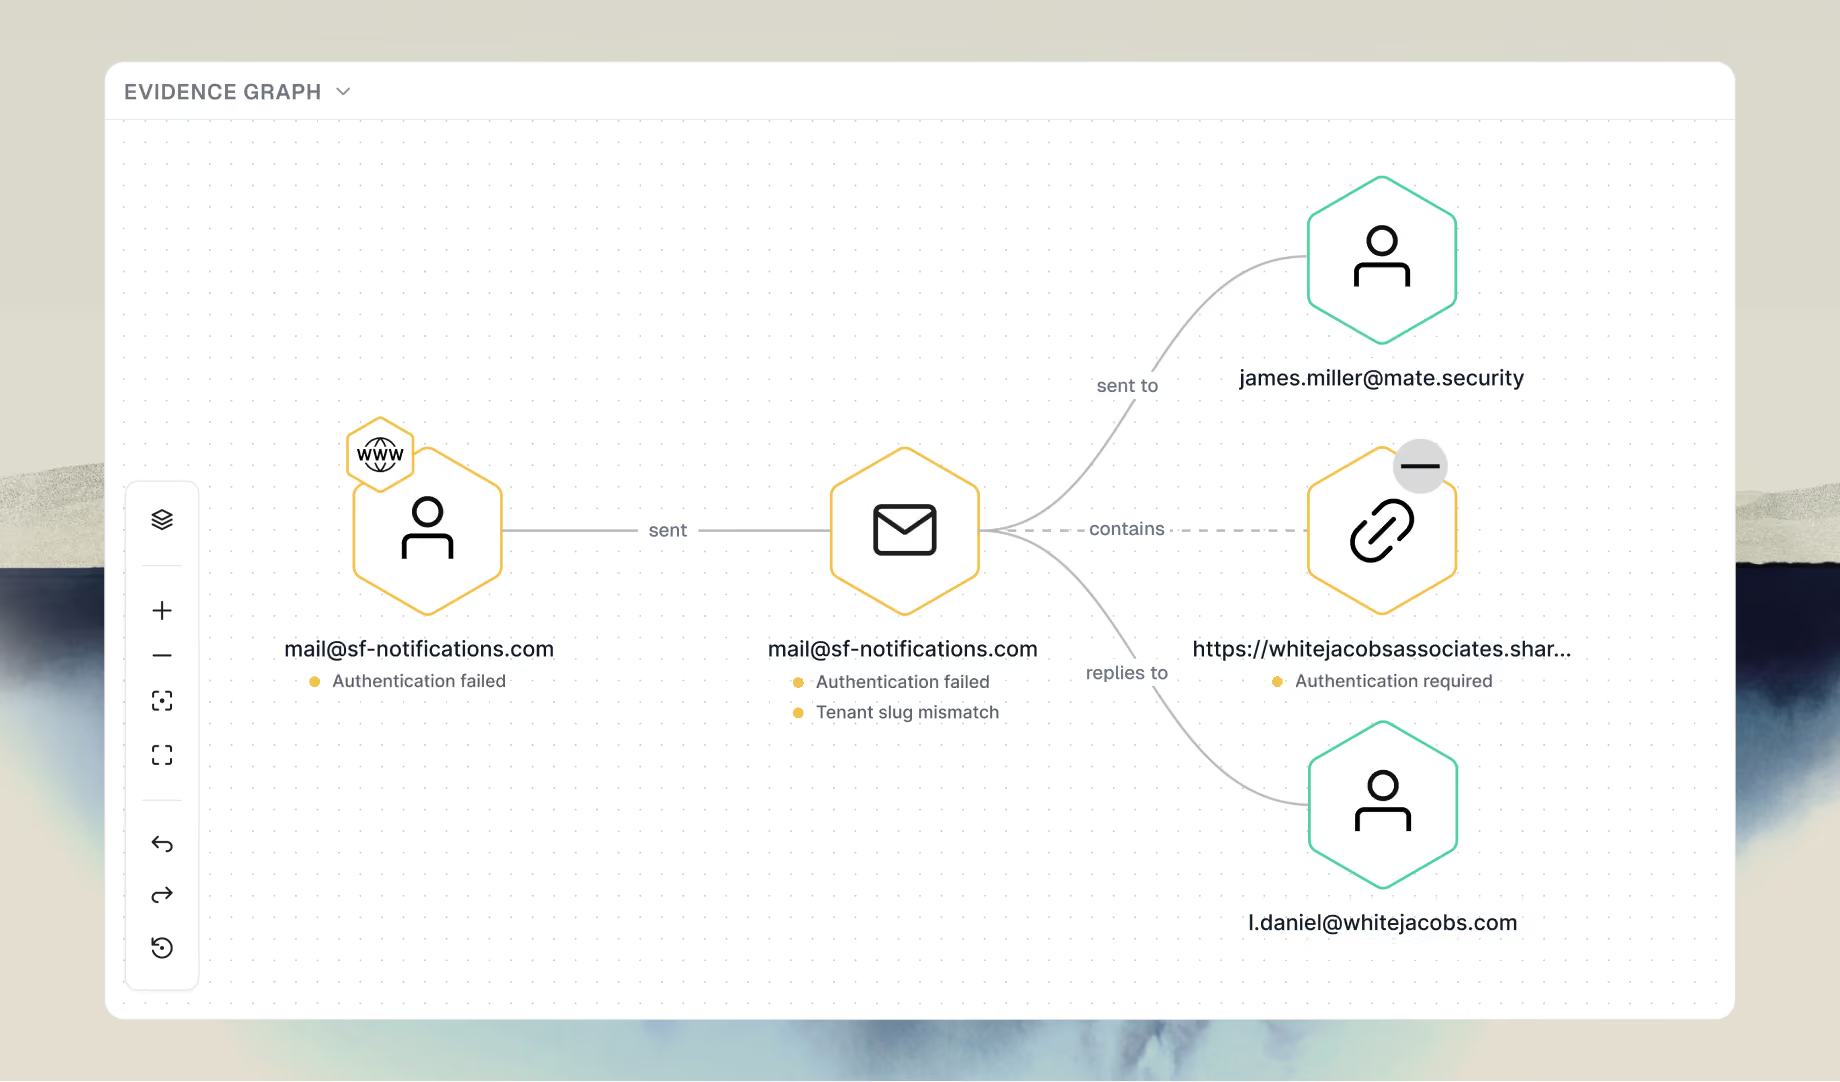
Evidence chain
Collects the artifacts, history, identities, and tool outputs an expert would check.

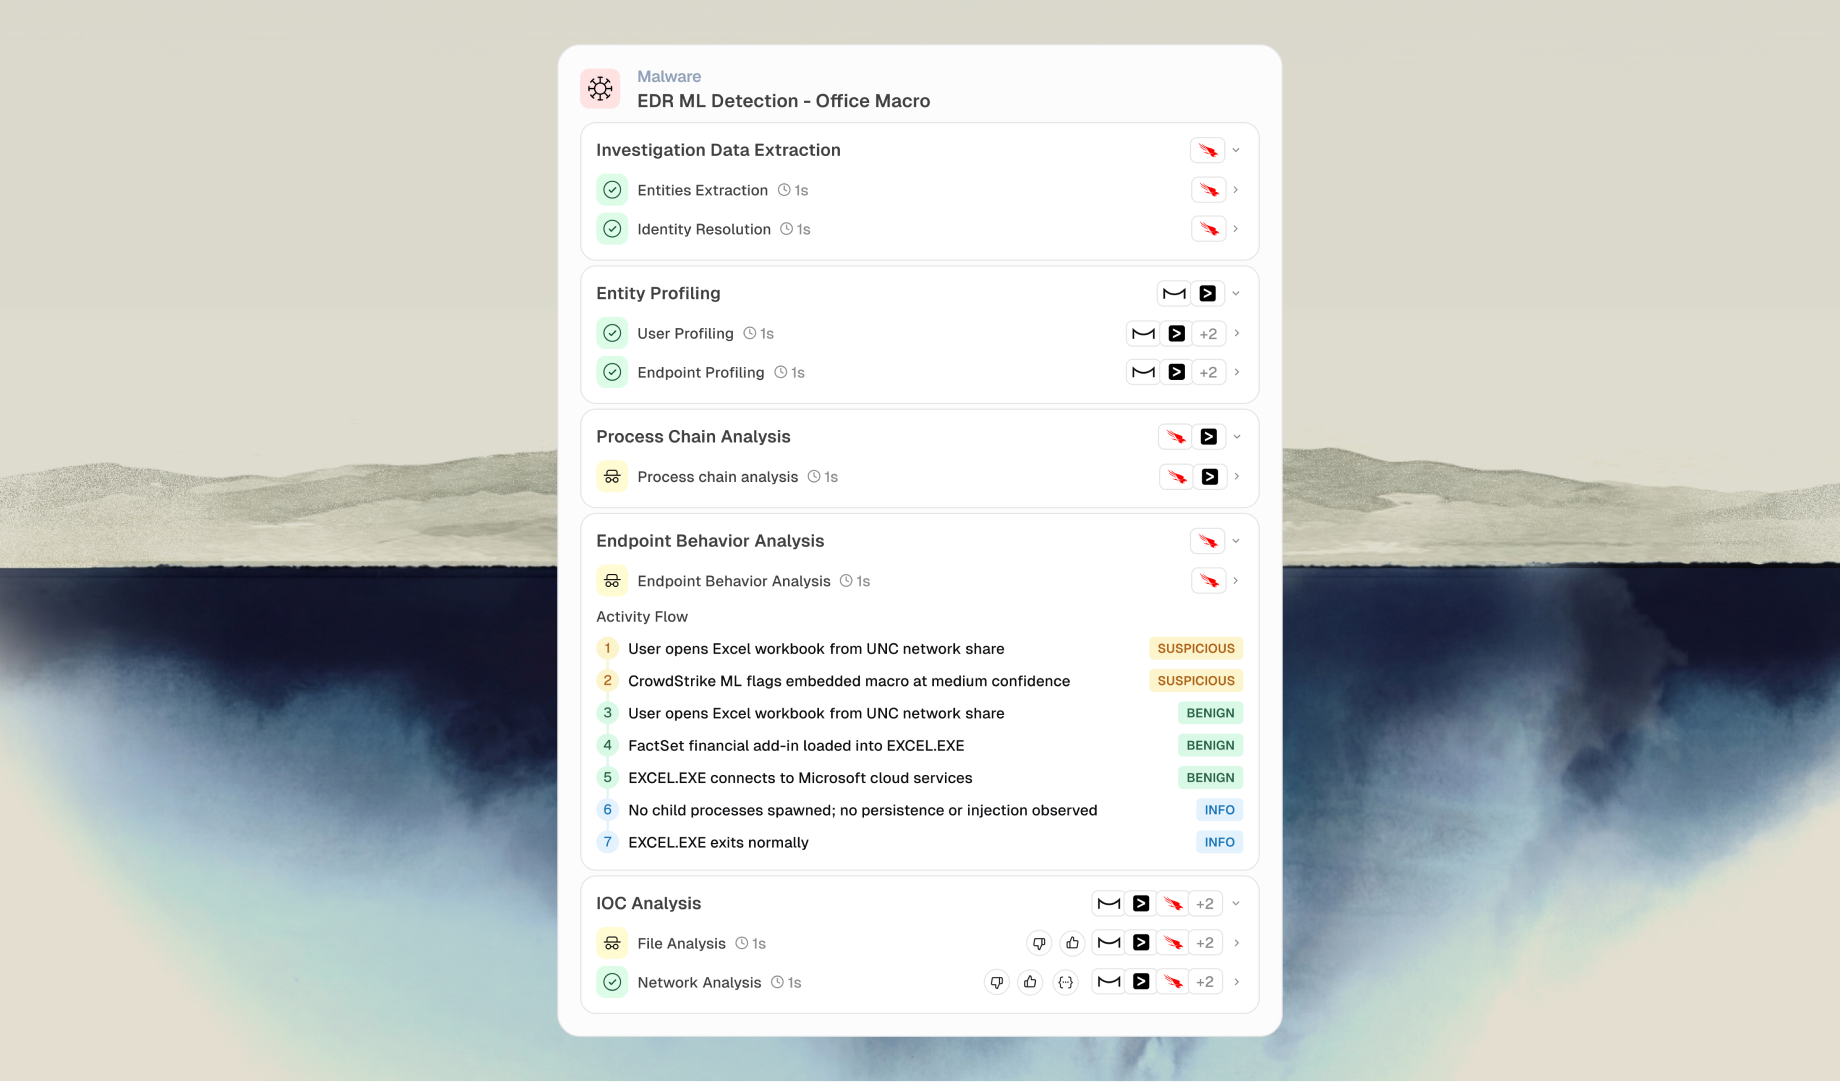
Expert reasoning
Applies domain-specific decision logic designed by analysts who worked these alerts in production.

Verified verdict
Returns a clear conclusion with the evidence trail your team can audit and tune.
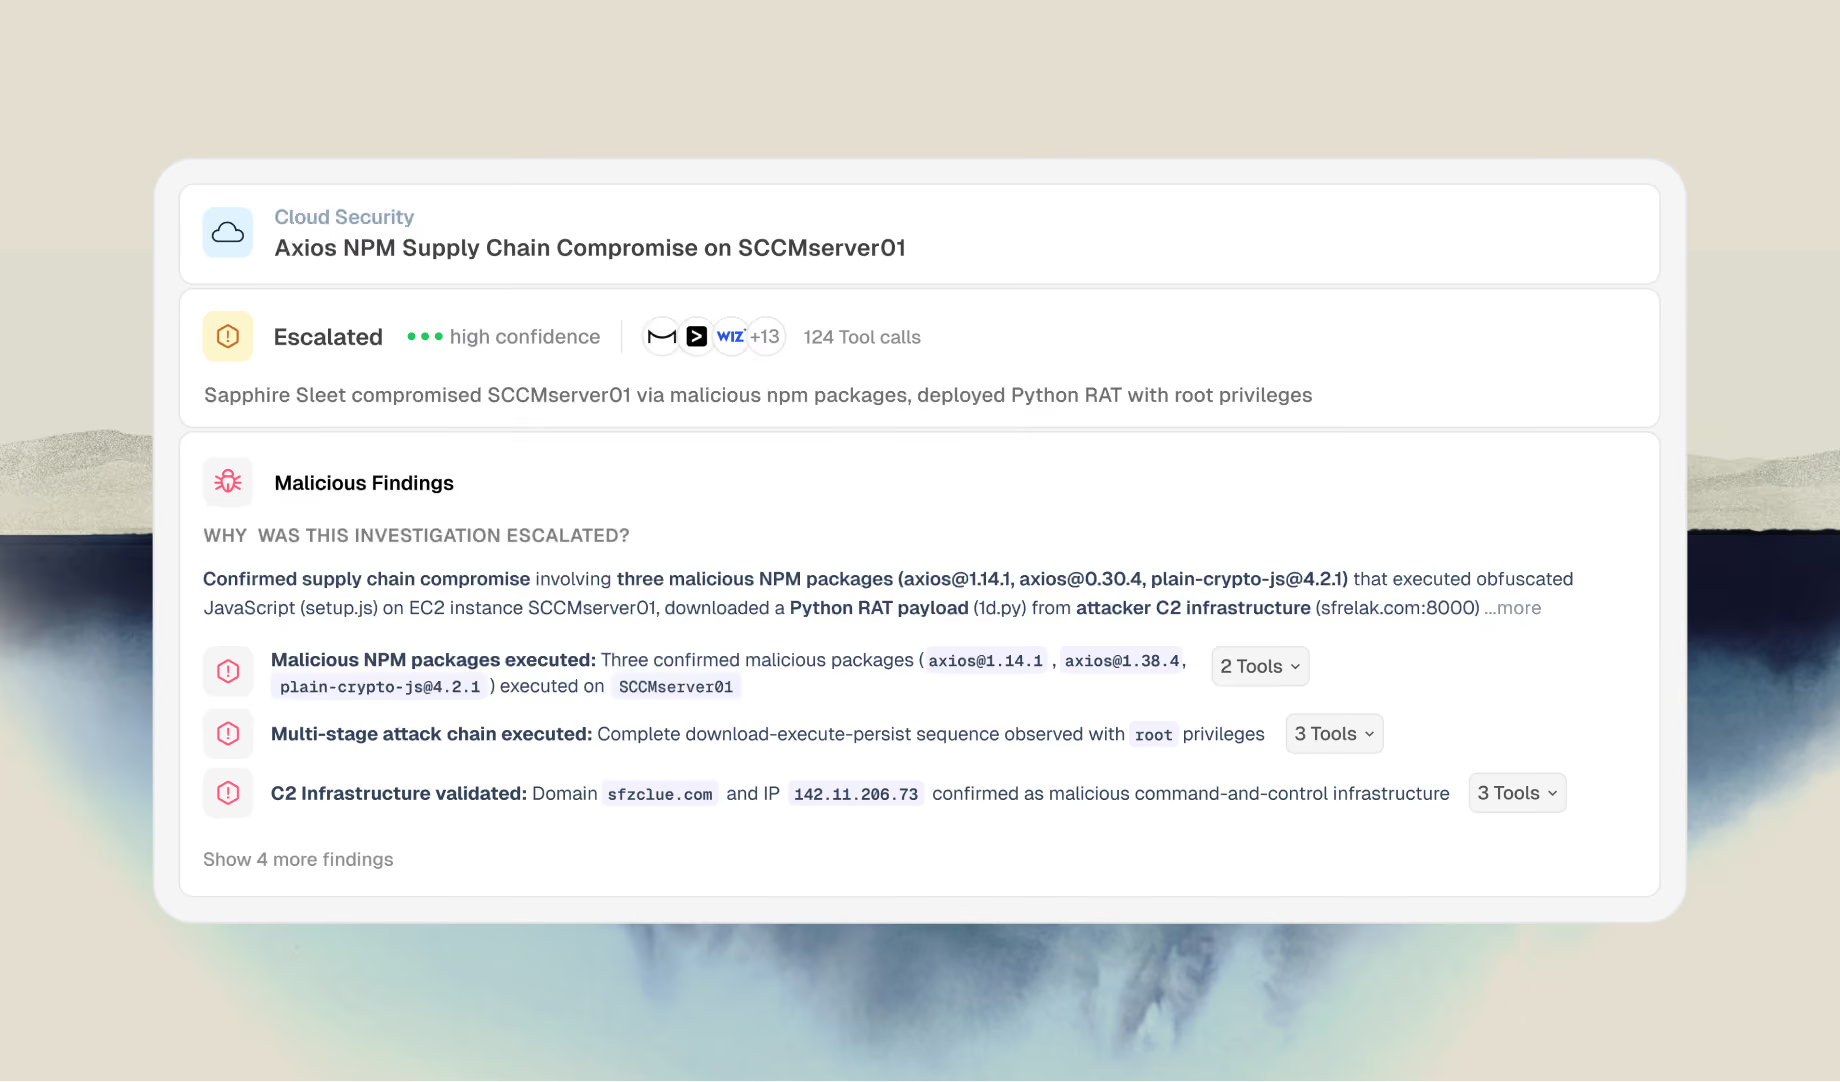


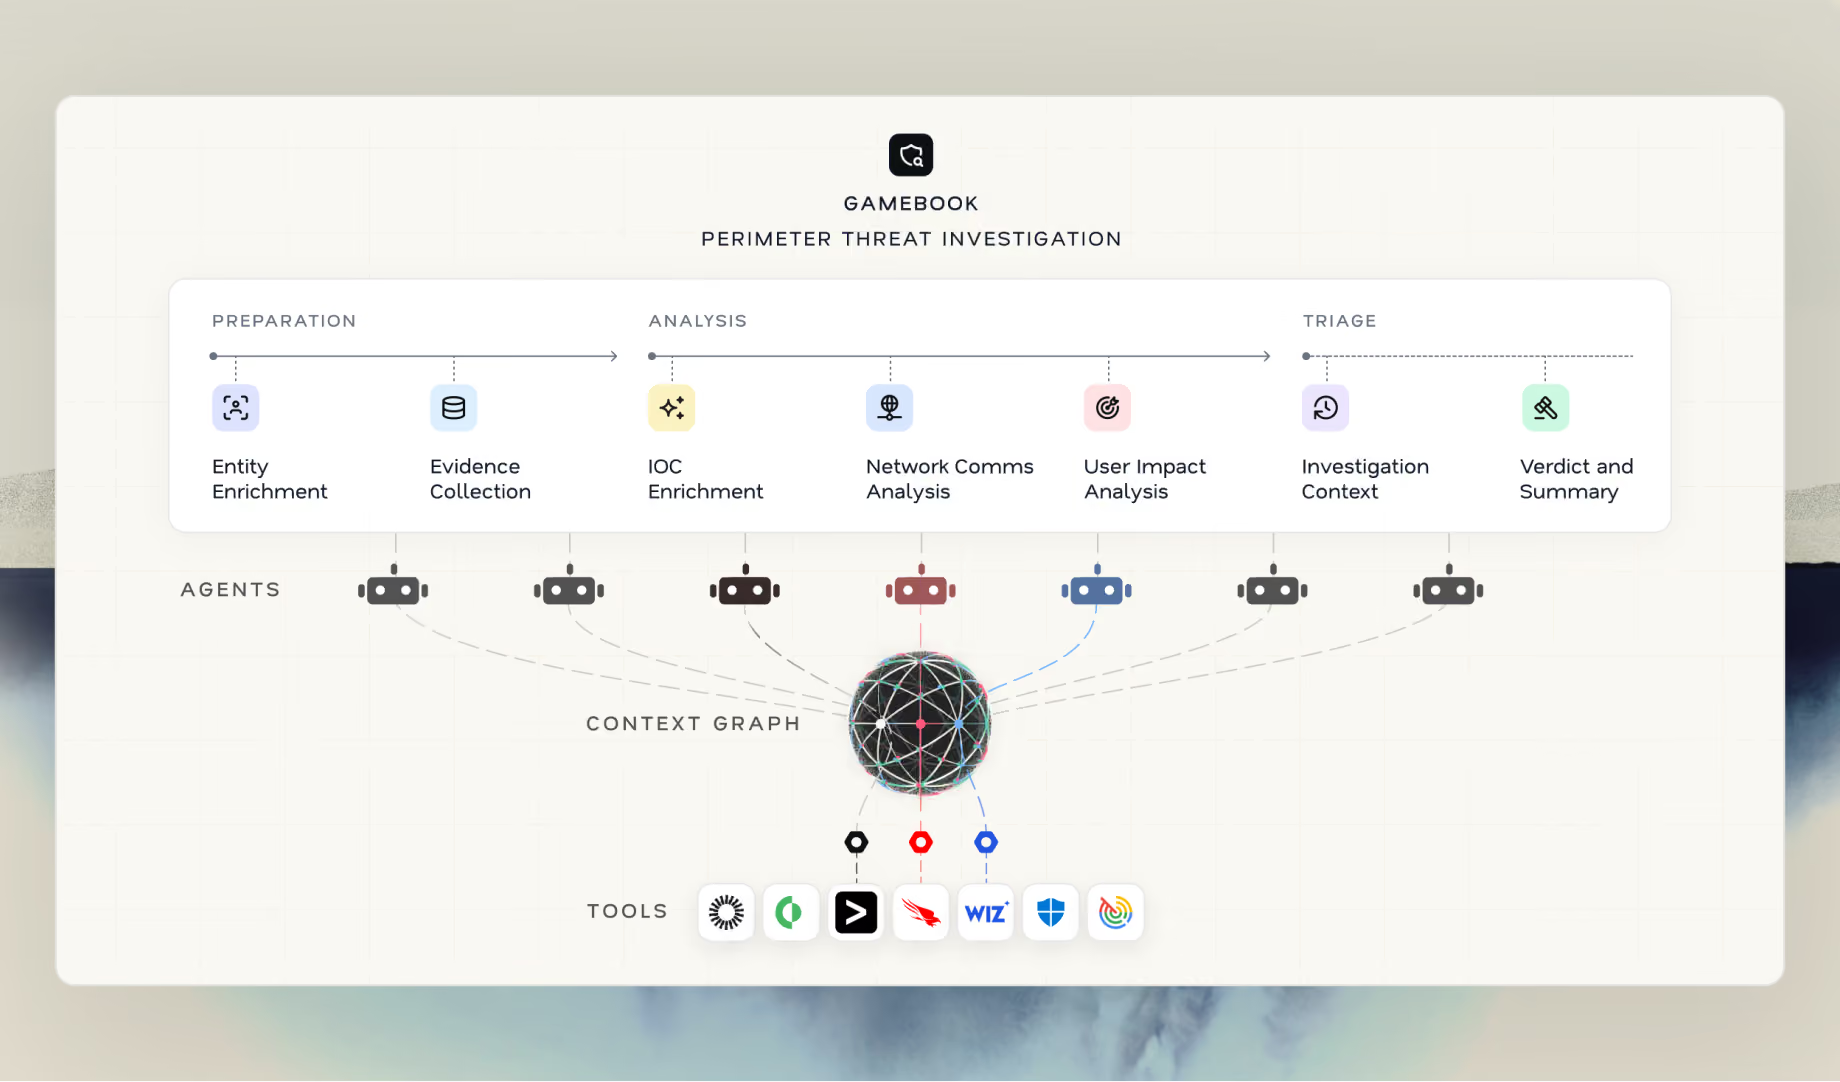
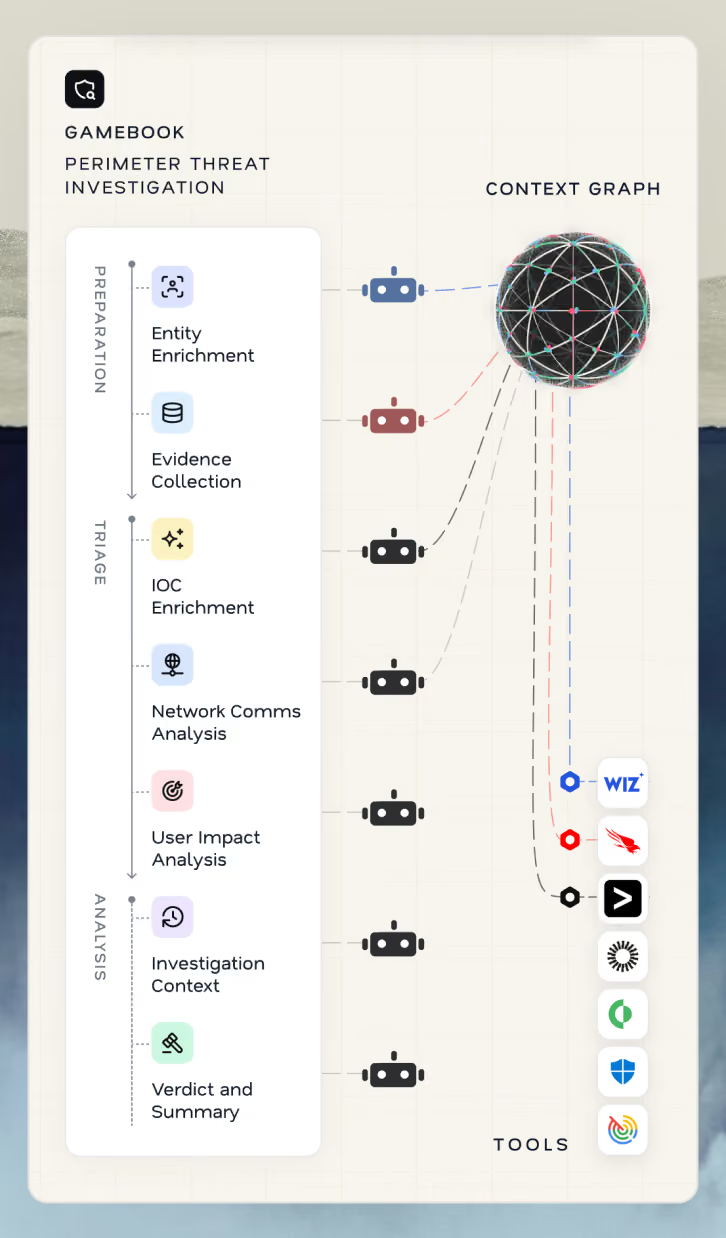
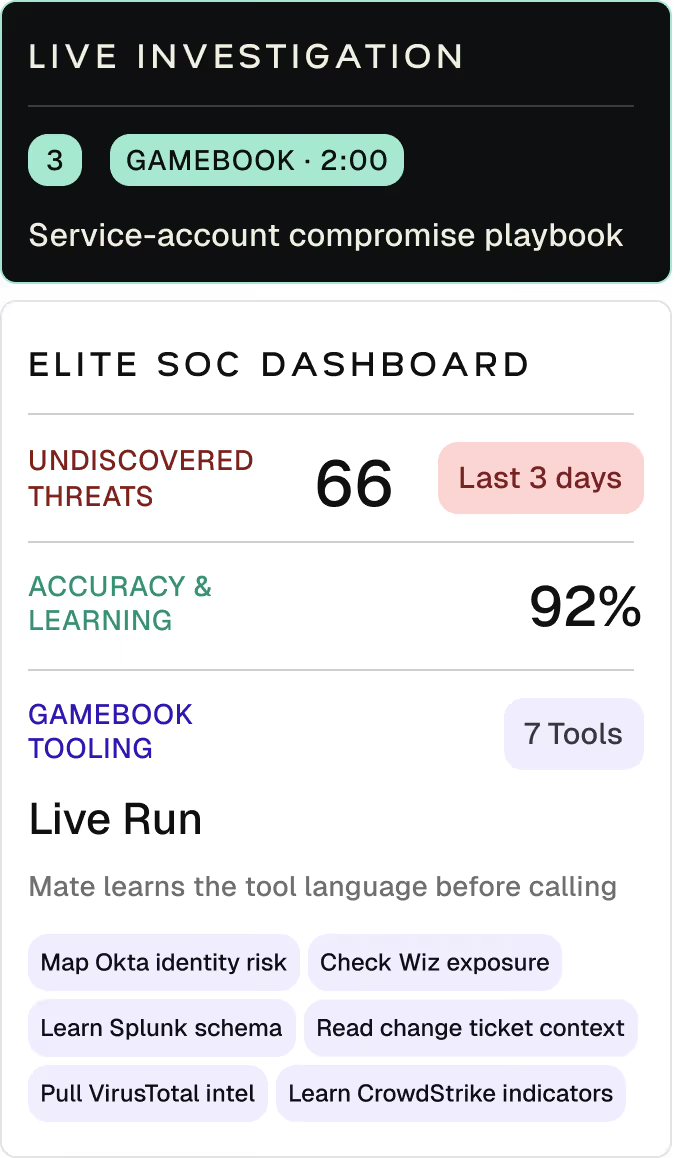
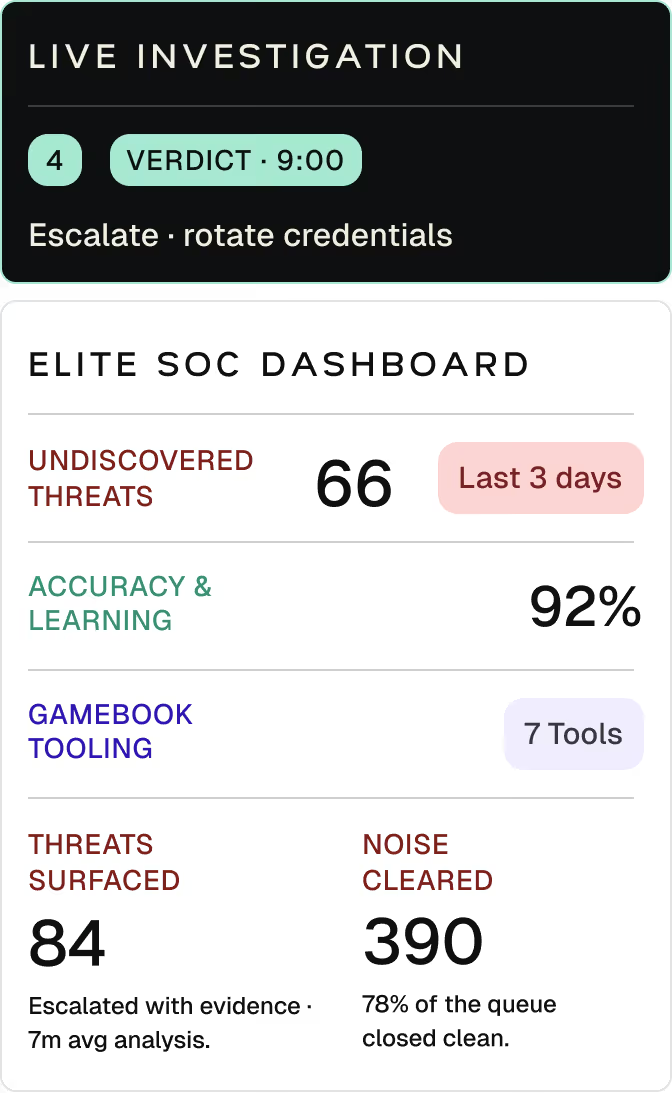
Gamebook-Driven
A structured investigation process where AI agents reason and pivot dynamically within every step
Security expertise meets tool mastery.
Mate understands the alert category, then works each tool like an expert analyst would.
Learn more →
Cloud
IAM drift, public exposure, cross-account trust, resource changes, and misconfiguration impact.

Insider risk
Behavioral deviation, peer-group baselines, HR signals, DLP context, and unusual data movement.

Business email
Forwarding rules, invoice changes, executive impersonation, vendor context, and mailbox history.

Endpoint
Process trees, LOLBins, file reputation, sandbox behavior, containment paths, and lateral movement.

Identity
Authentication baselines, JIT access, MFA bypass, privilege escalation, and risky login patterns.

Phishing
Mailbox analysis, sender checks, QR patterns, campaign clustering, URL detonation, and user impact.


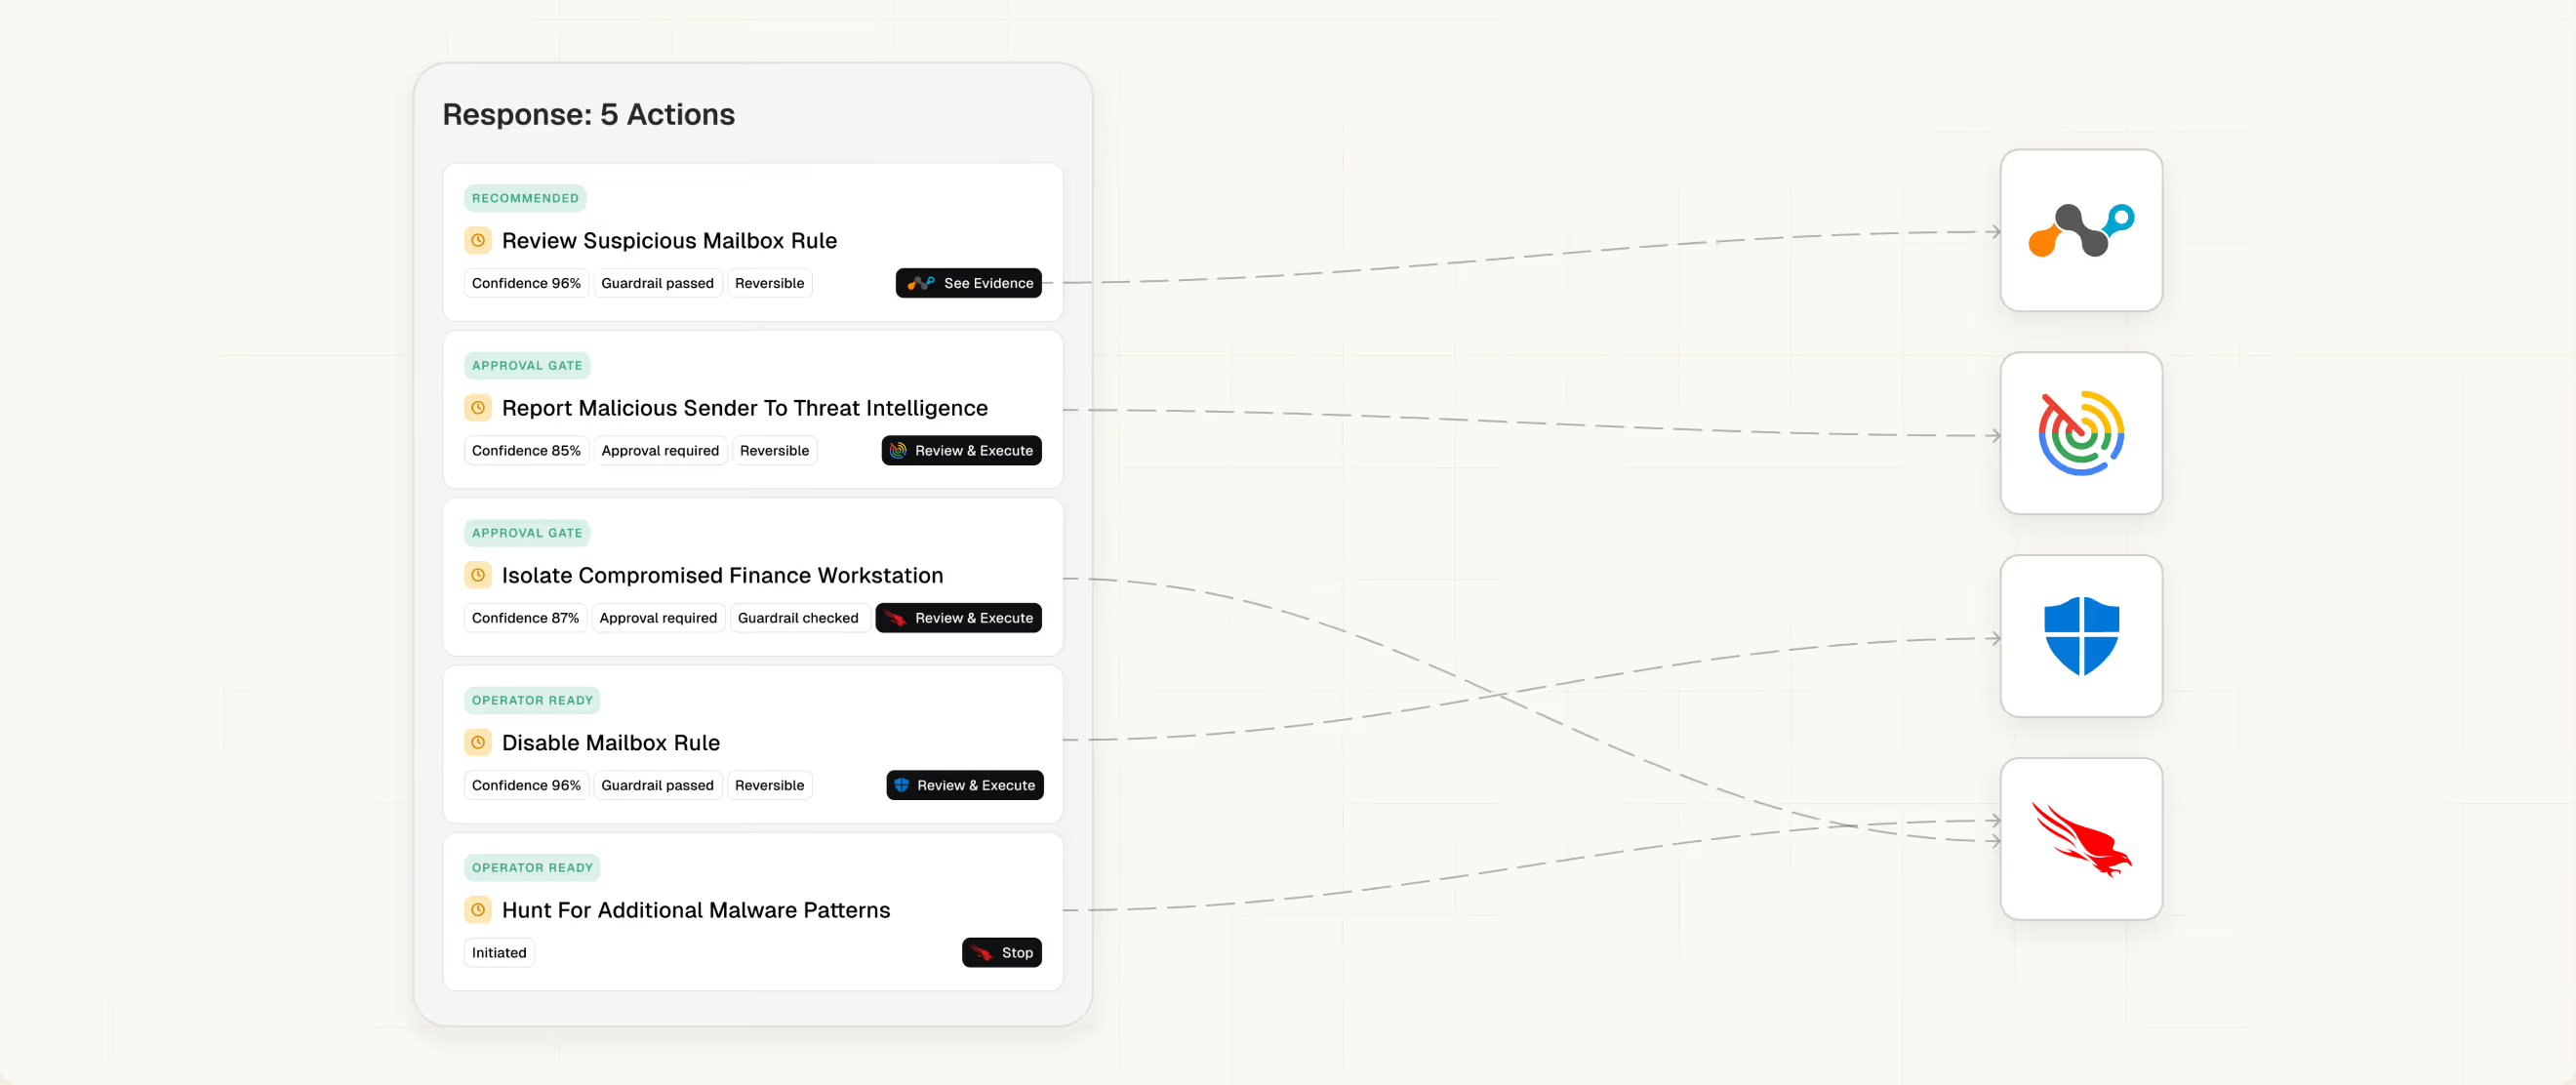
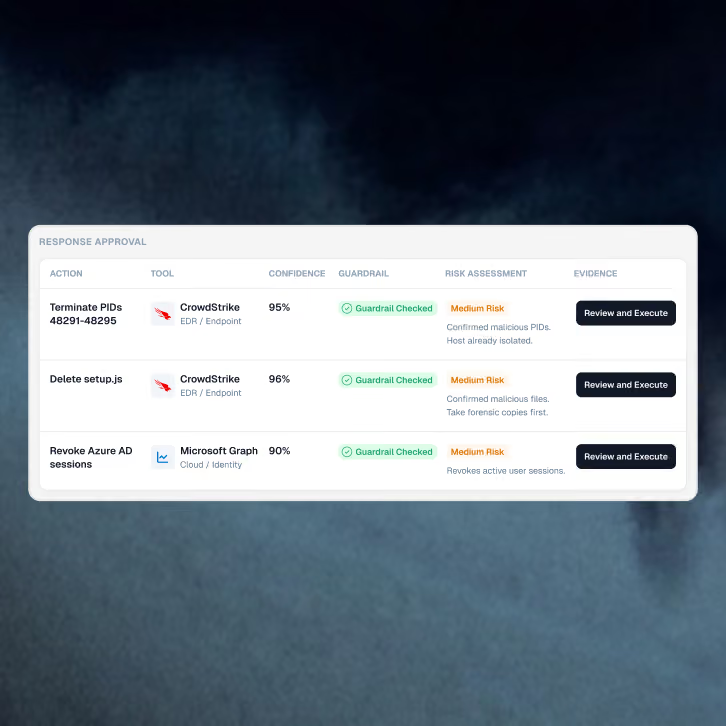
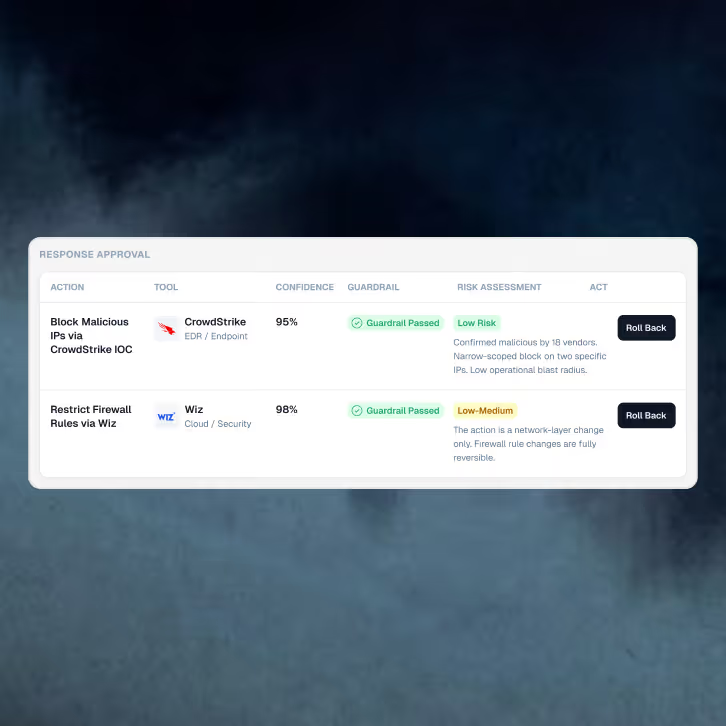
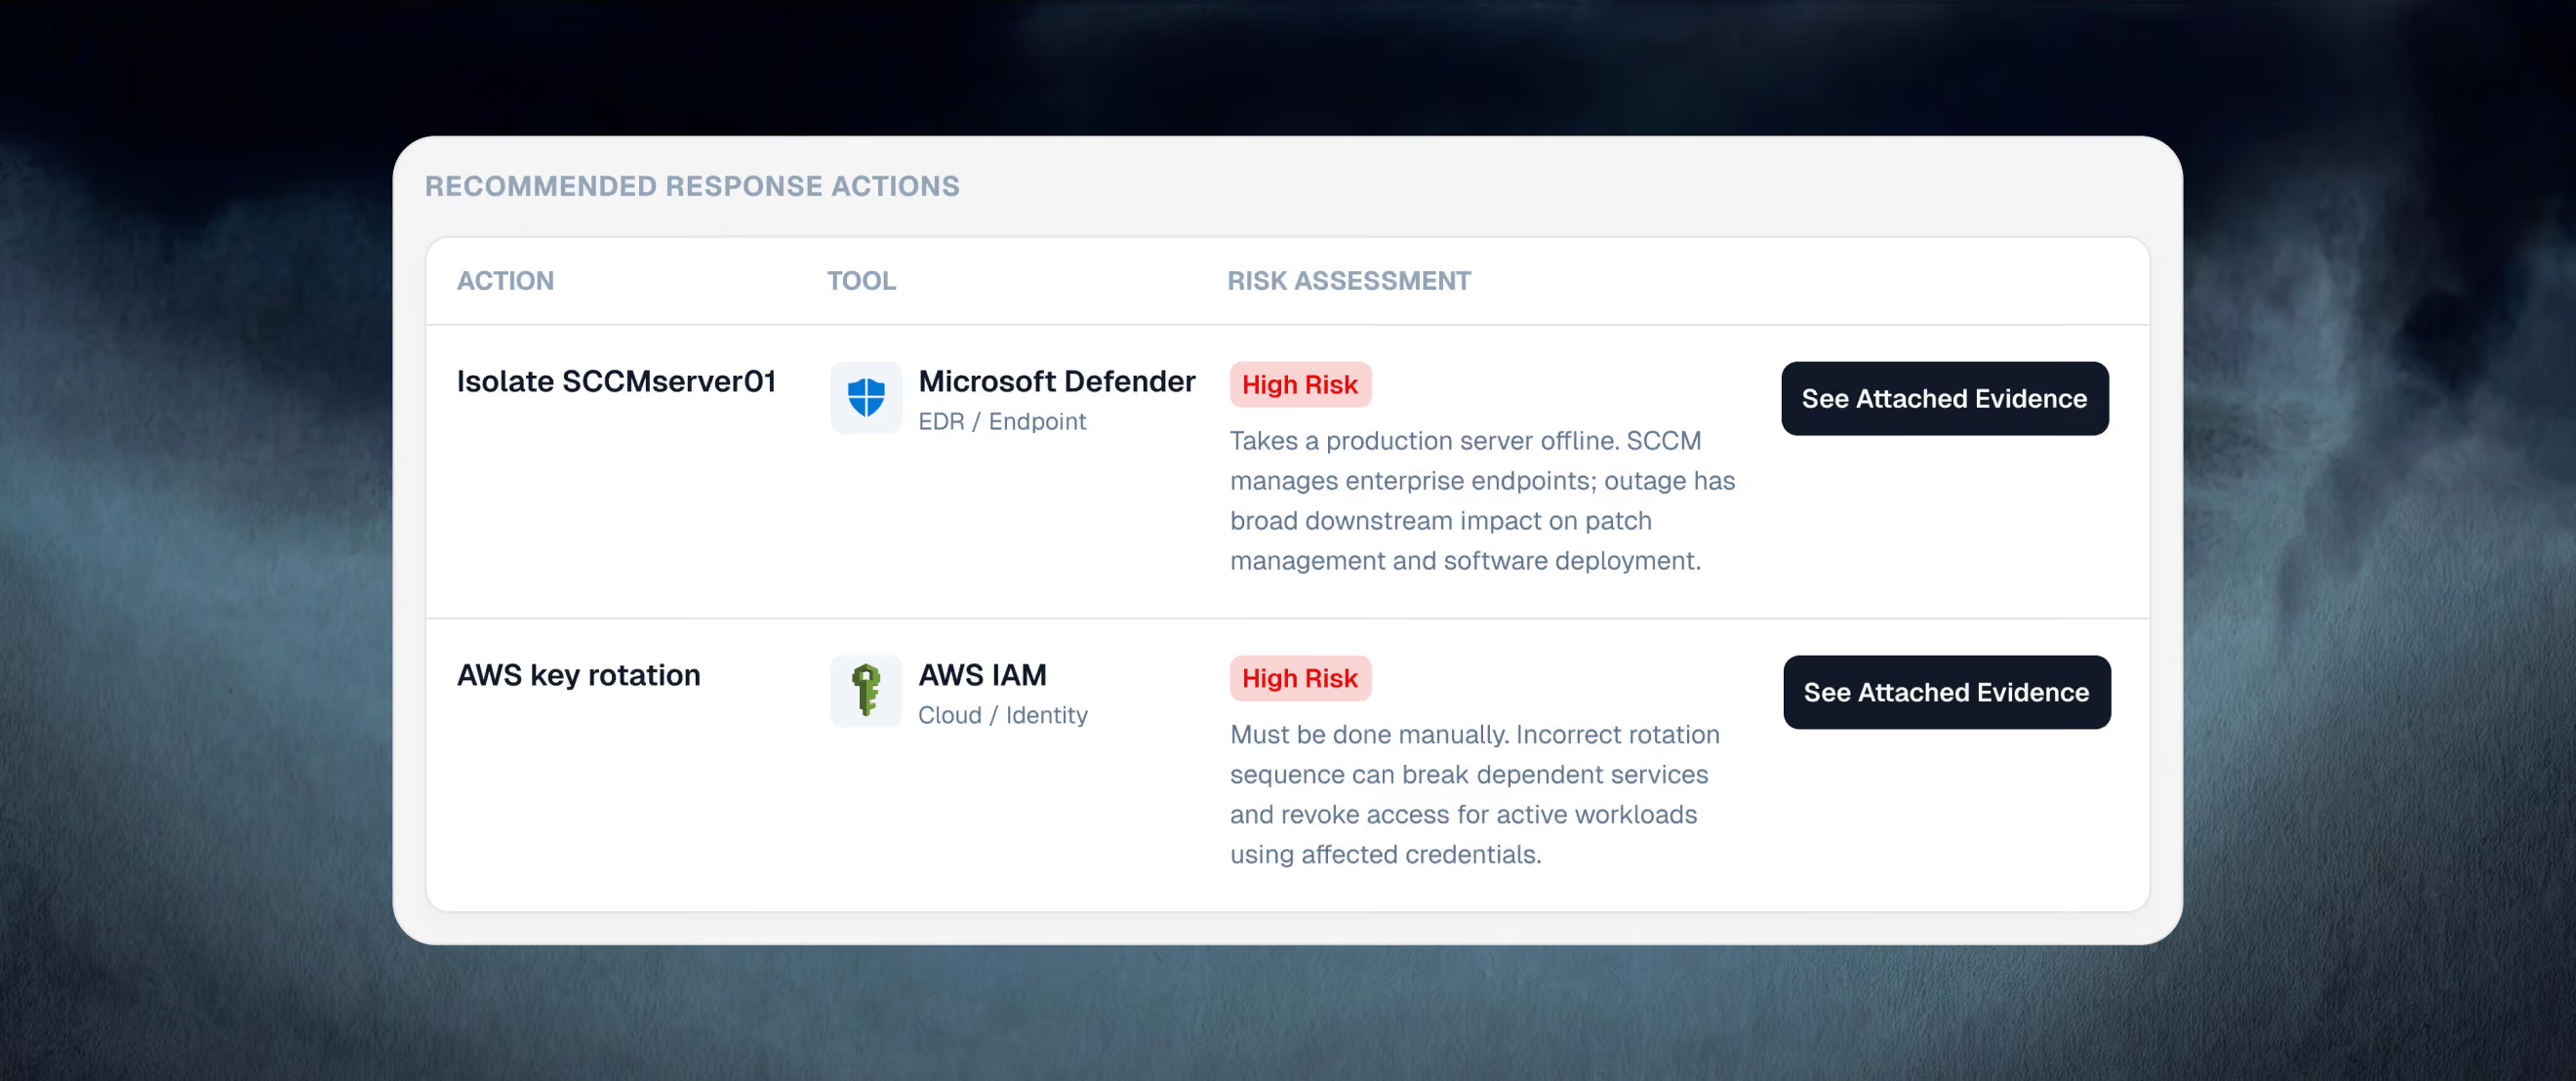
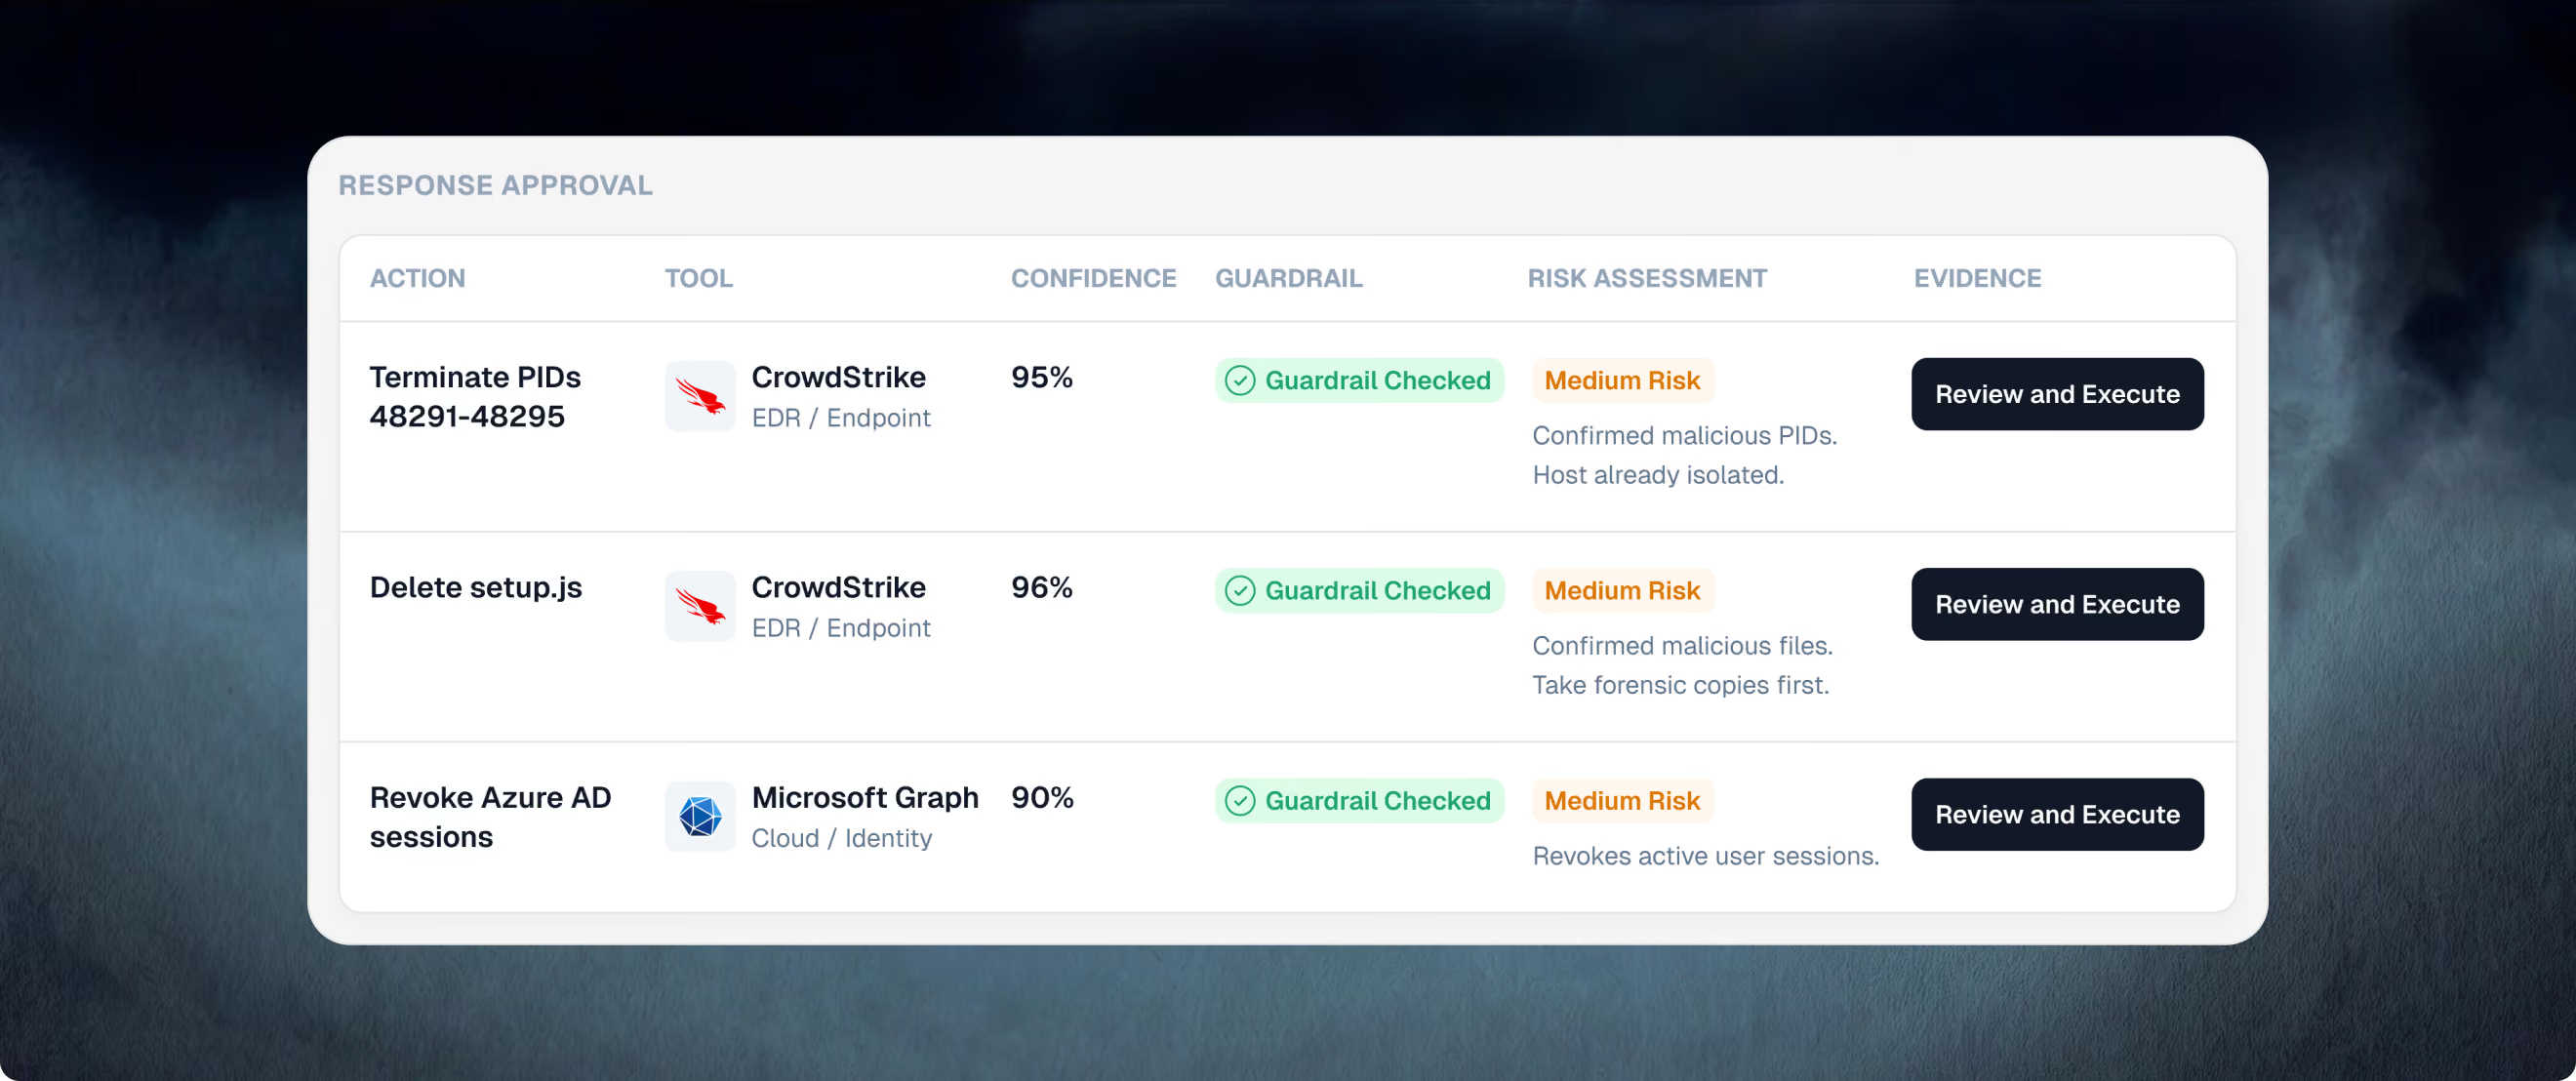
Response you can trust at machine speed.
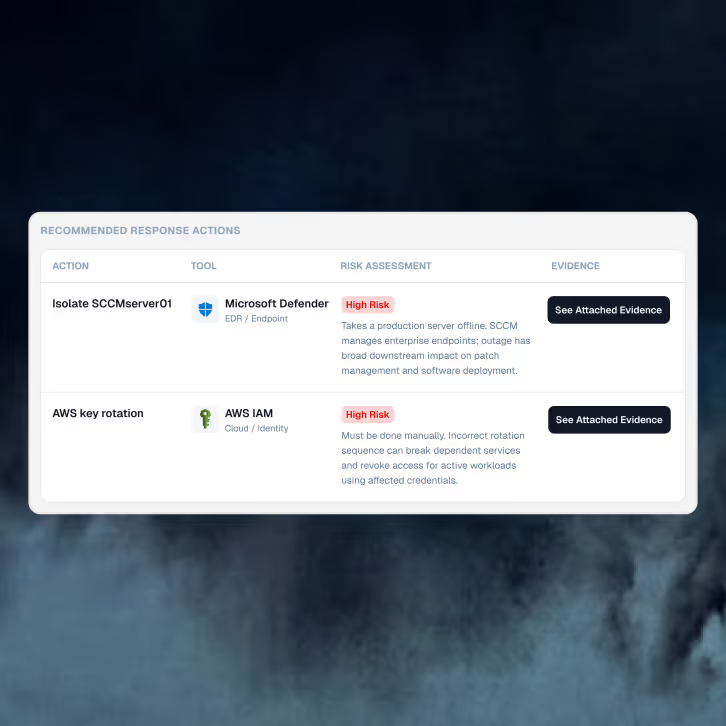
Mate checks every action against your environment before it runs. Threats get contained in minutes without taking the business down, and autonomy grows one action class at a time.
Learn more →Recommend only
Mate investigates and recommends.
Your team decides what can run.
Supervised
Trusted low-risk steps can run.
Risky changes still ask.
Auto-run
Trusted categories run end-to-end
under guardrails and audit.

Cpr: Three checks before every action.
Every action is scored on Confidence, Precision, and Reversibility. The platform enforces this outside the agent's reasoning loop, so Mate can't widen its own permissions, hide its actions, or grade its own accuracy.

Confidence
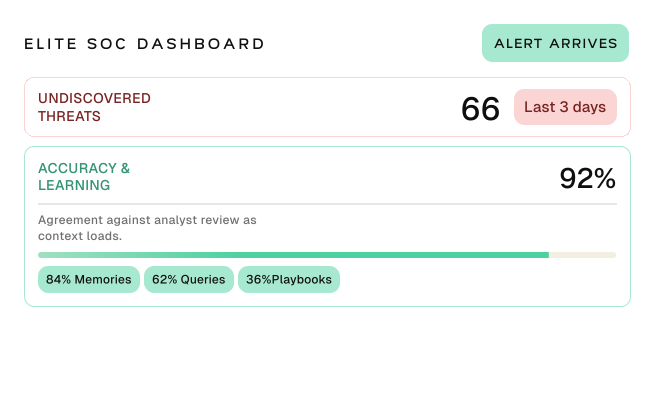
Earned from Mate's track record on cases like this one. If accuracy drifts, that category drops back to Supervised.

Precision
The smallest action that stops the threat. Revoke the session, keep the account.

Reversibility
Mate knows what it can roll back, and sets a higher bar for what it can't.
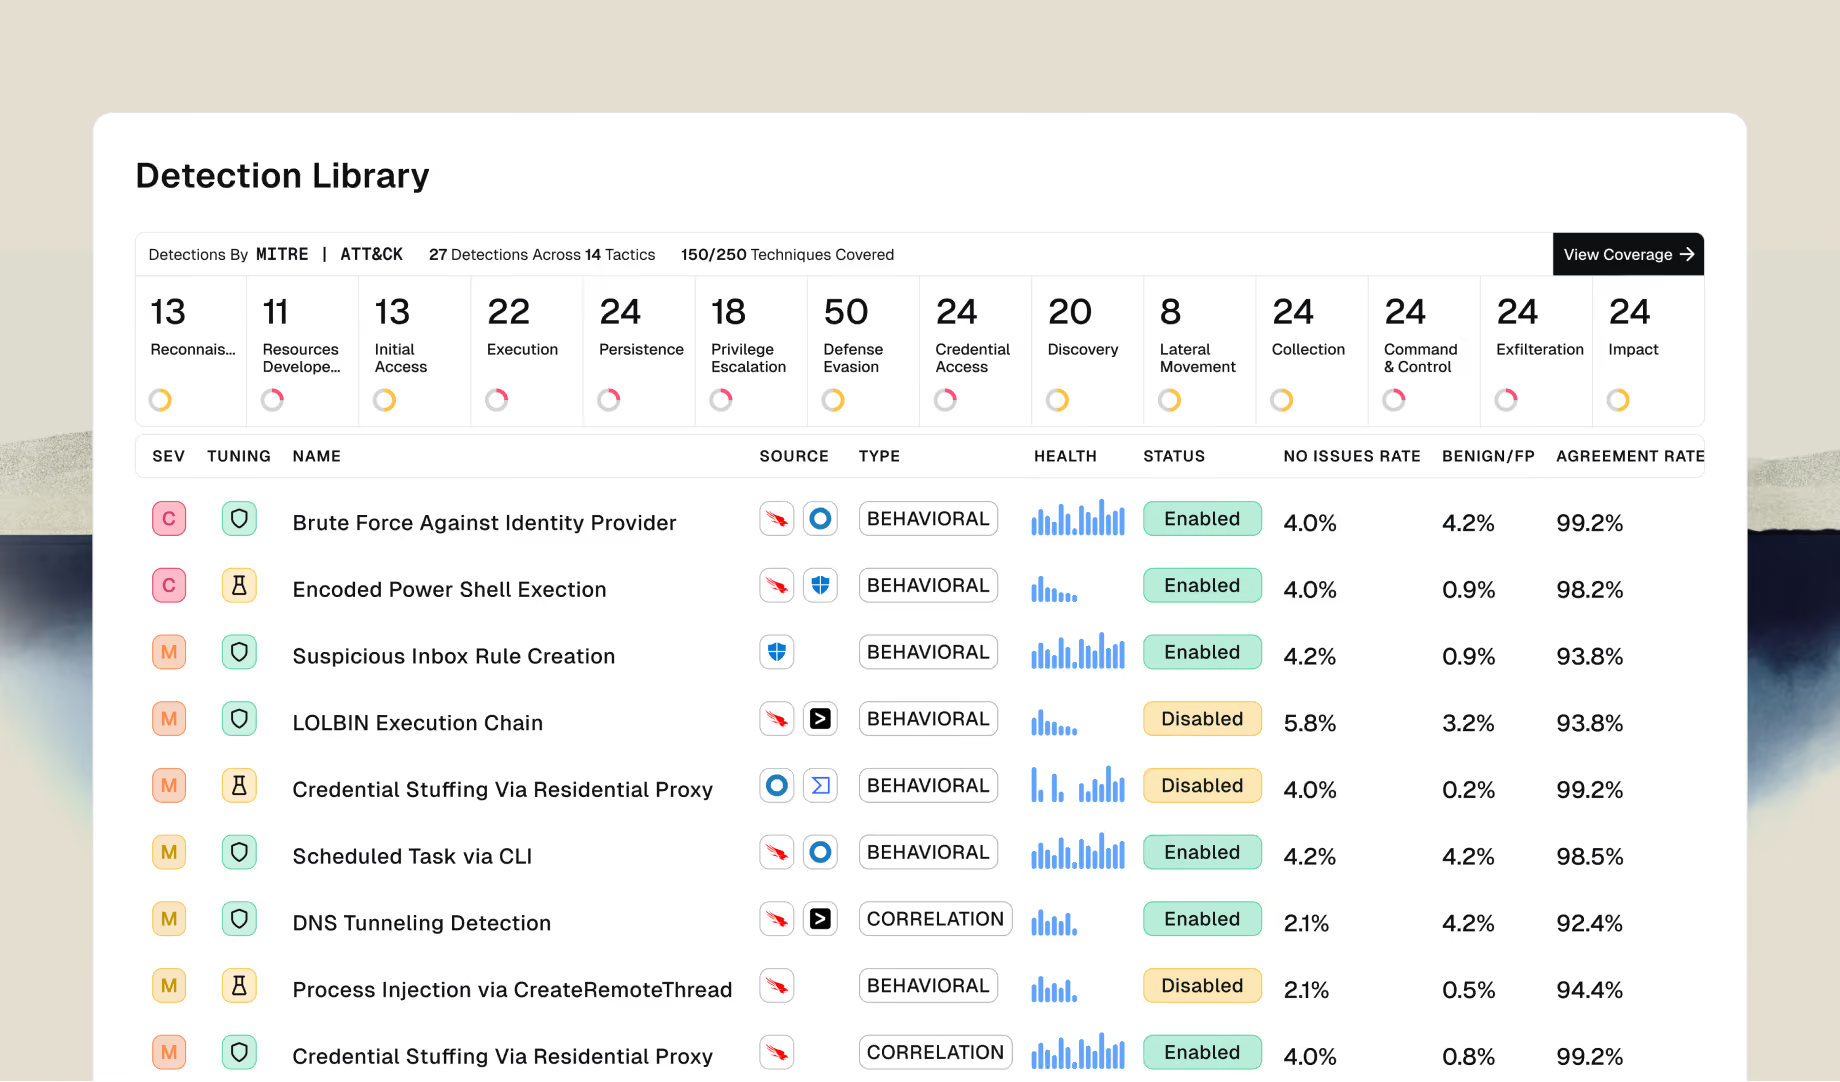
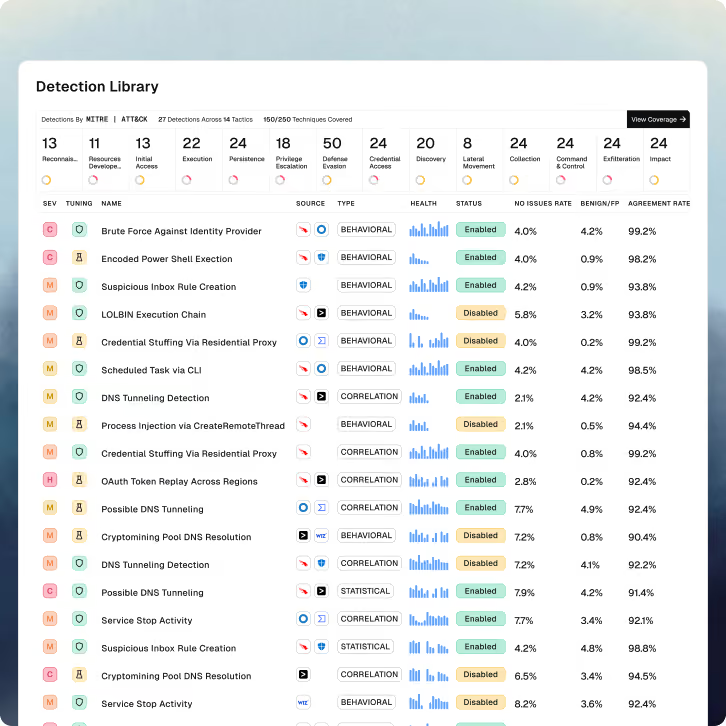
Detection Engineering that Continuously Tunes
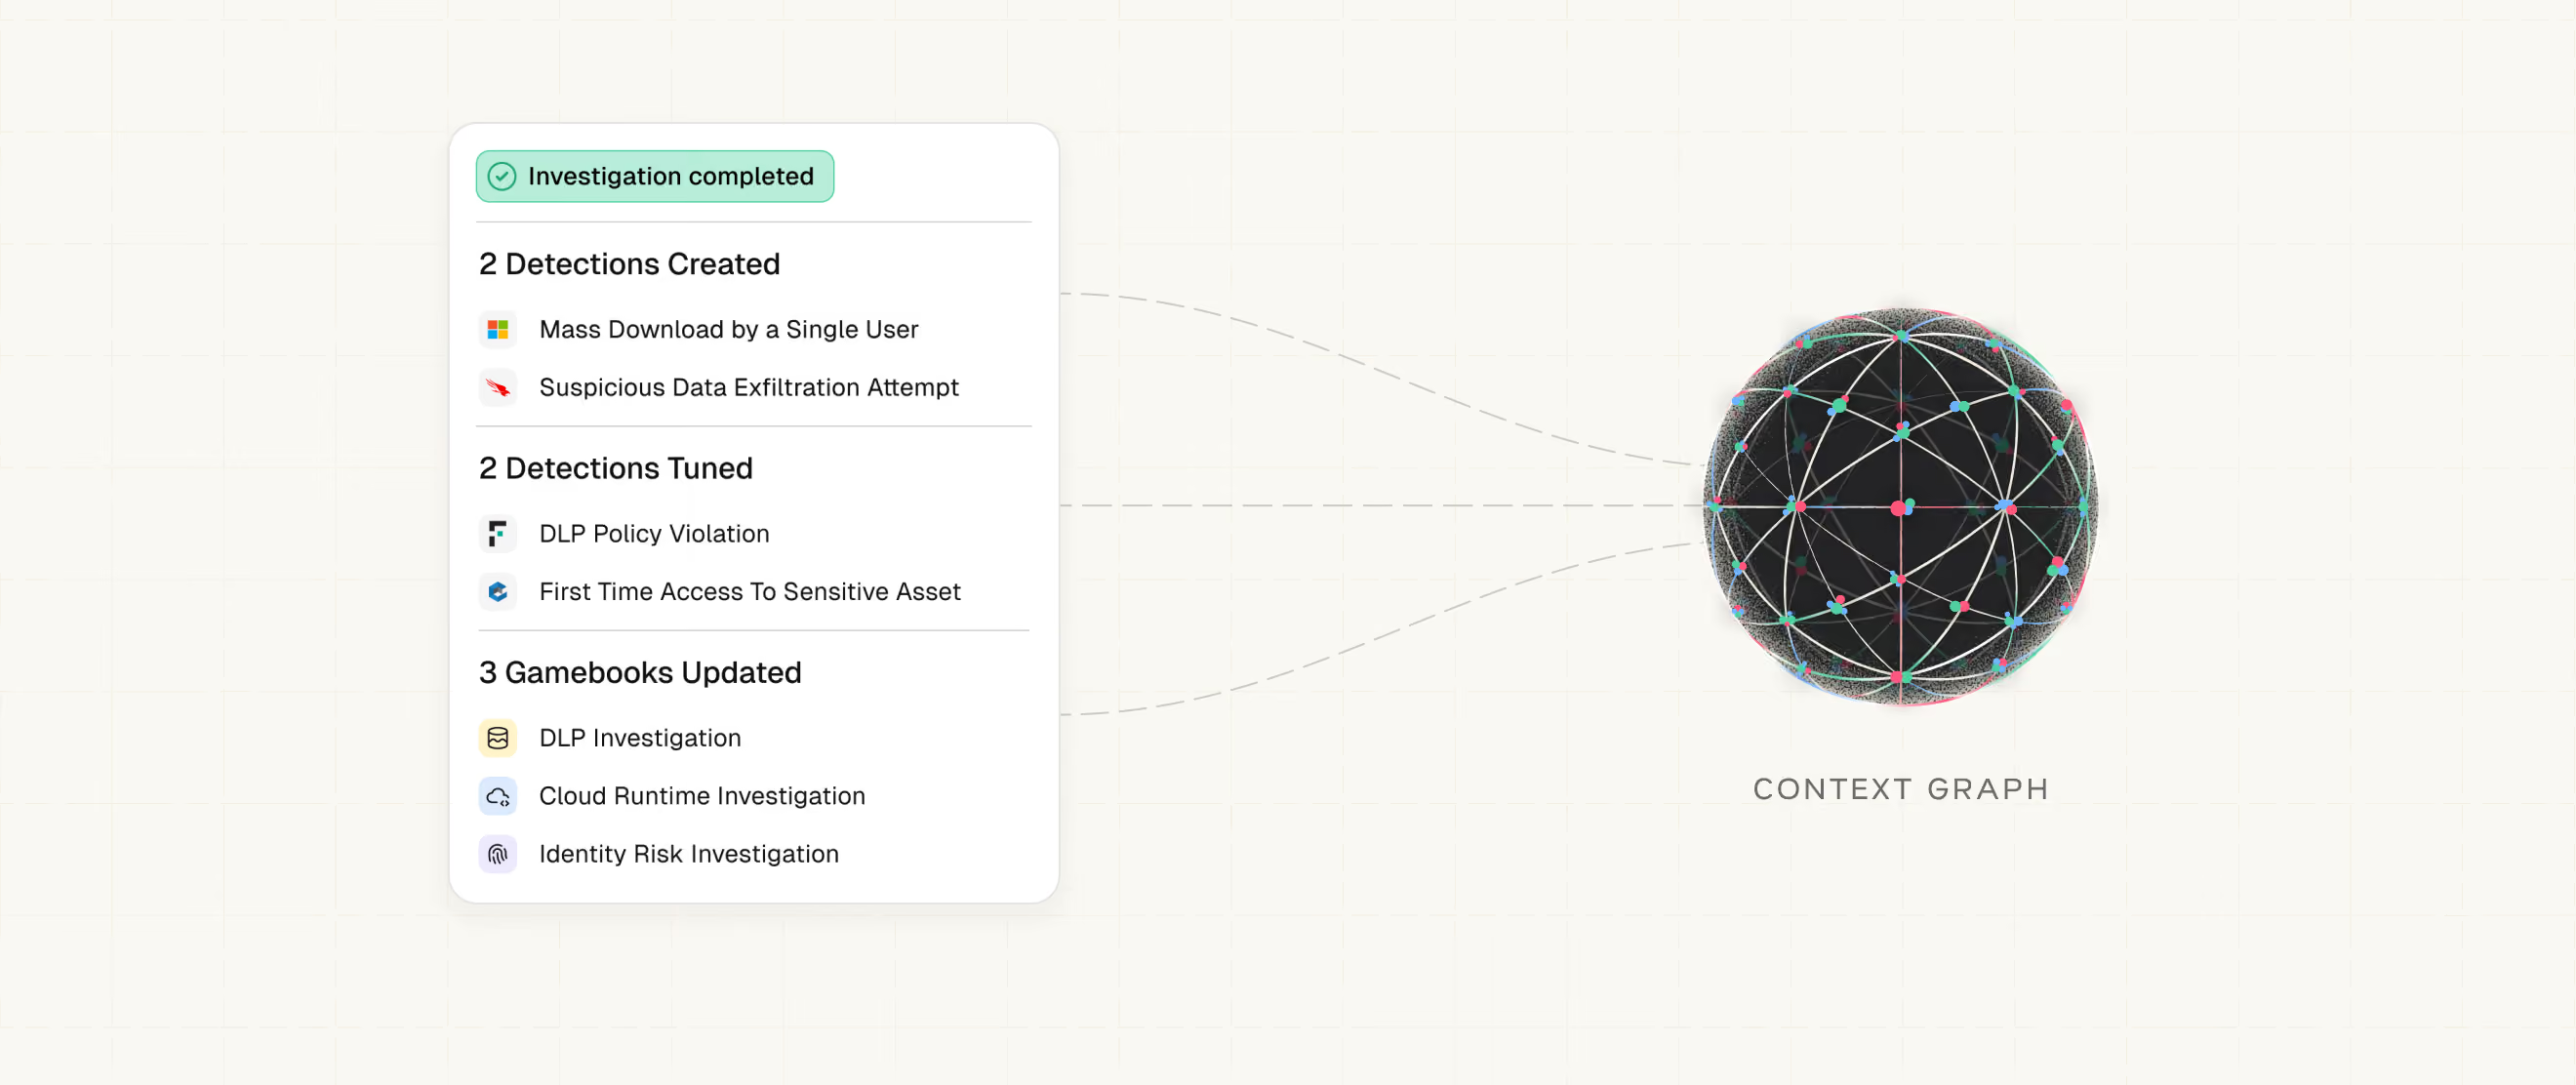
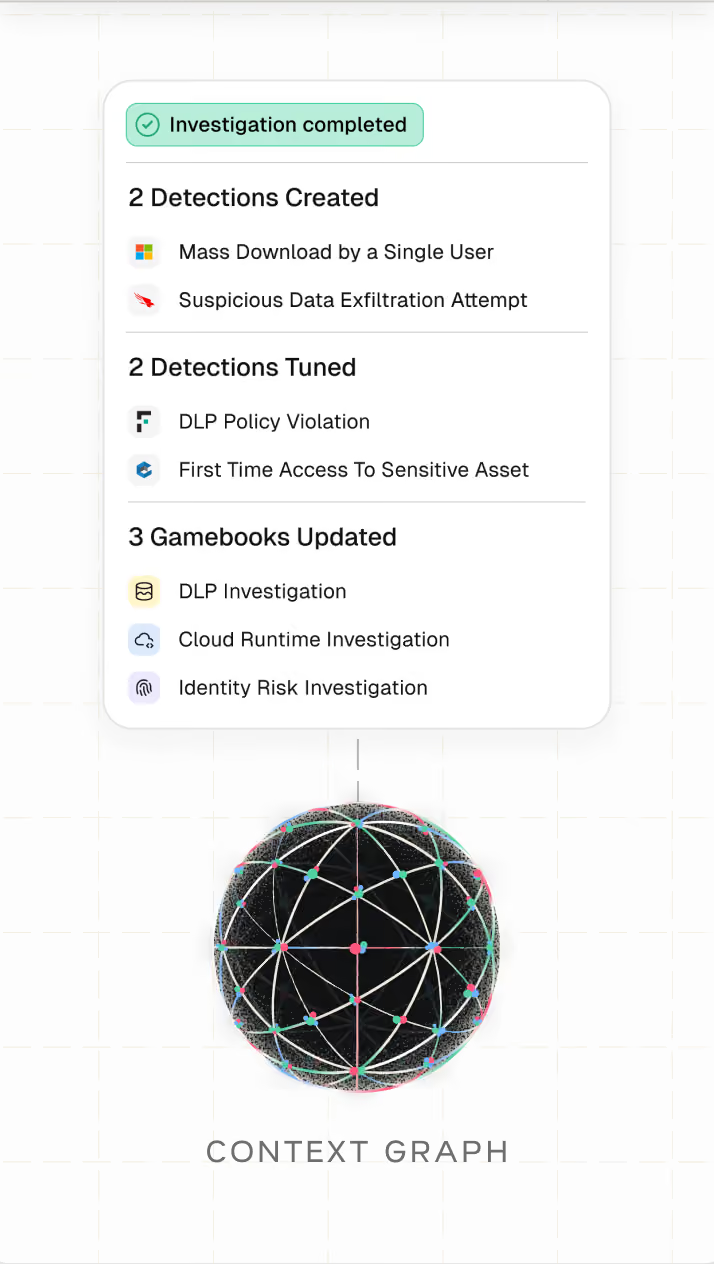
Detections are continuously created, tuned, or deprecated based on investigation outcomes and contextual changes, maximizing coverage and relevance.
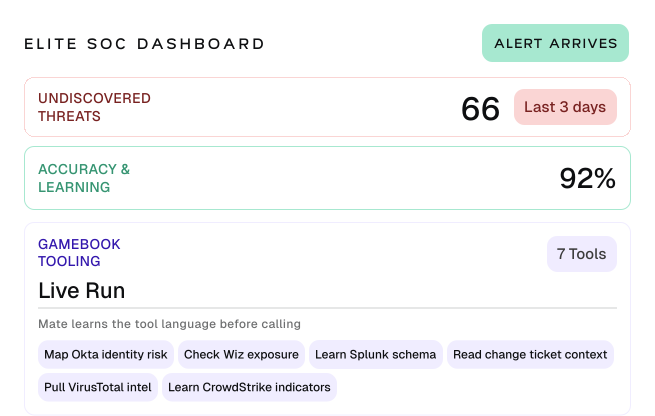
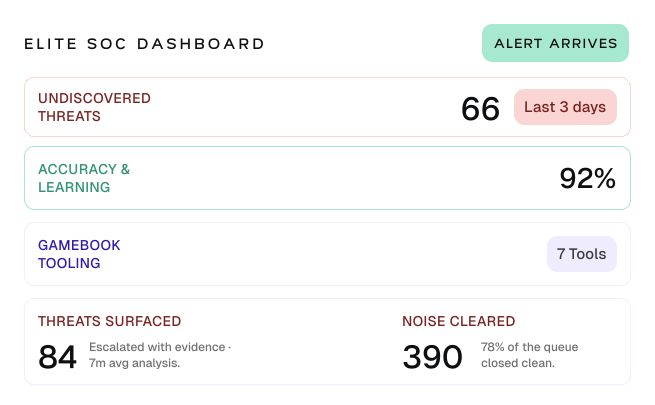
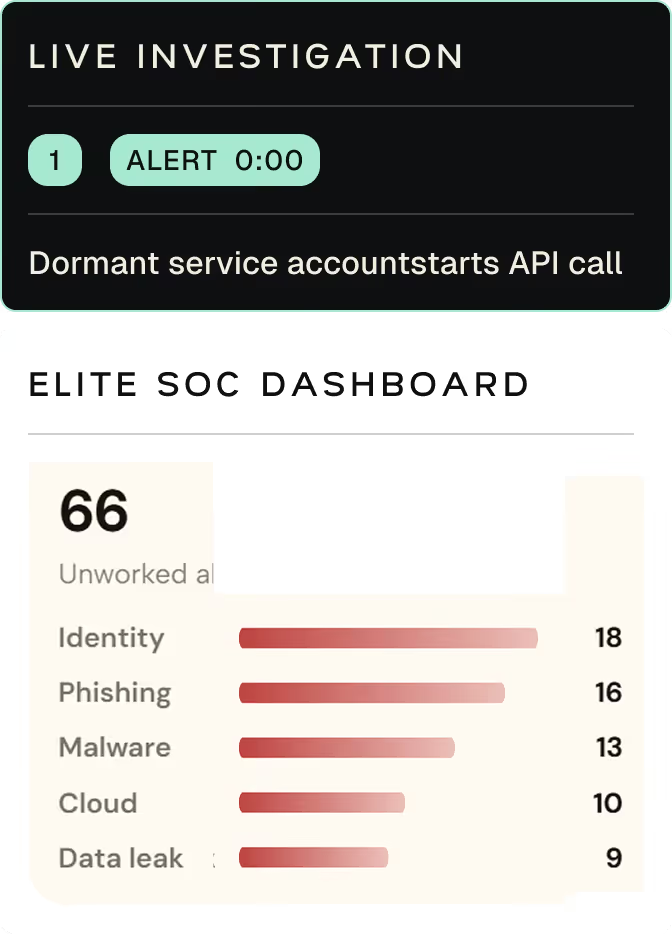
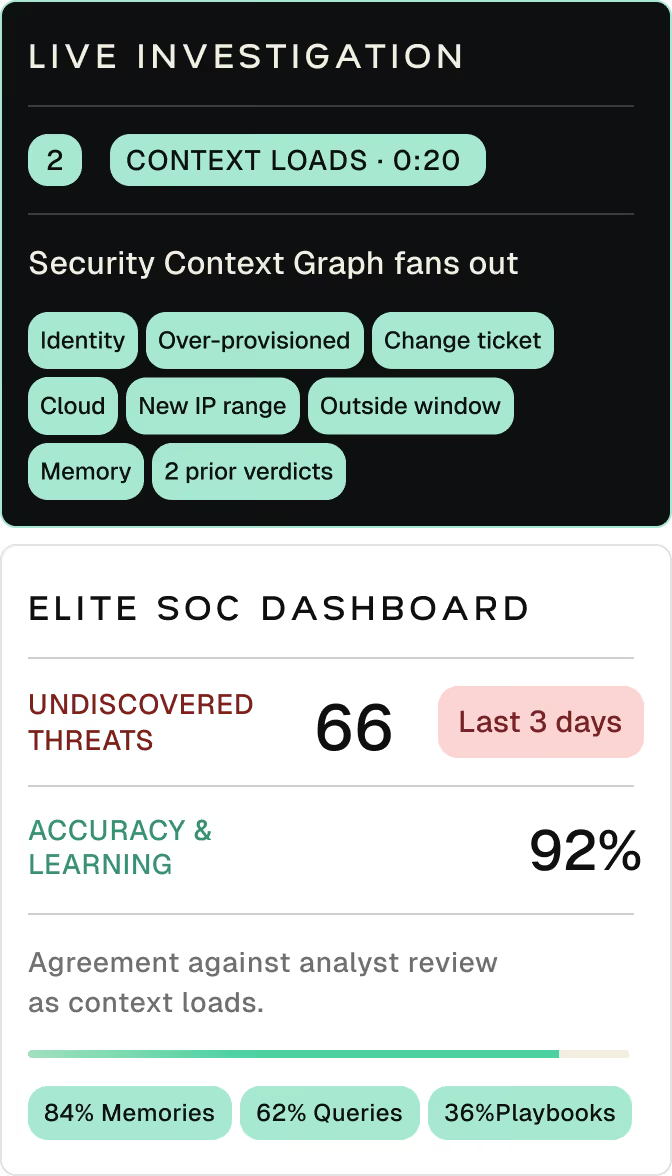
Gamebooks: Make Them Yours
Building agentic workflows is hard. With Mate you get elite gamebooks out of the box, and bring your own knowledge in two ways, no rip and replace:
Bring your playbooks
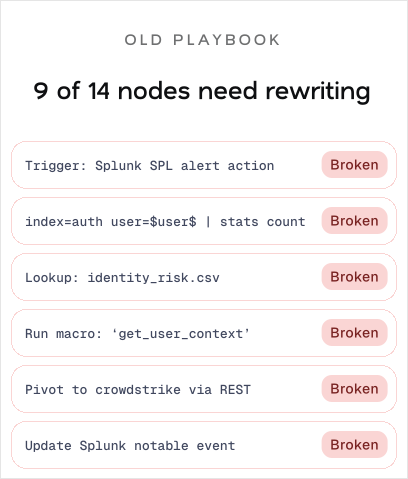
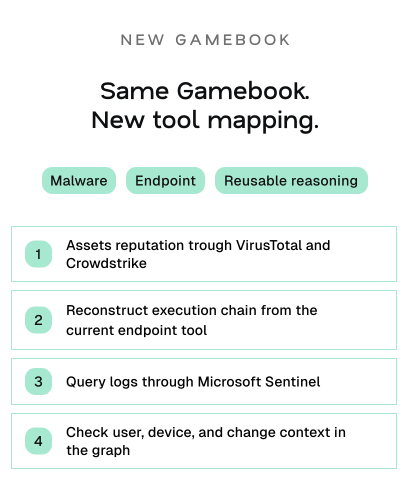
Mate translates your SOAR playbooks into Gamebooks. Brittle API calls get replaced. Your custom logic stays.

Describe what you need
Gamebooks are extendable by design. Write the investigation in plain language. Use your Workflows, 3rd Party Tools, 1st Party Tools and Best of Breed Agents. Mate tests it against past cases, runs it in shadow mode, then waits for your sign-off.
Gamebooks work through changes
Your reality keeps changing. Gamebooks keep working because they are driven by intent and Mate’s context graph, not hard coded API calls and individual knowhow.
SOAR playbooks
vs. Mate gamebooks
You swap your EDR
CrowdStrike becomes SentinelOne.
Every node tied to CrowdStrike breaks.
The Gamebook doesn't change.


6 of 12 nodes need rewriting.
New vendor, new APIs, new playbook.


Zero changes needed.
Same Gamebook. New connector swapped in automatically.